Frequently Asked Questions
Product Information & Features
What is Akeyless and what does it offer?
Akeyless is a cloud-native SaaS platform designed for secrets management, identity security, and encryption. It centralizes the management of secrets (API keys, passwords, certificates), secures human and machine identities with Zero Trust Access and Universal Identity, and uses patented Distributed Fragments Cryptography™ (DFC) for zero-knowledge encryption. The platform automates credential rotation, certificate lifecycle management, and integrates with tools like AWS IAM, Azure AD, Jenkins, Kubernetes, and Terraform. Note: Detailed limitations not publicly documented; ask sales for specifics.
What are the key features of Akeyless Secure Remote Access (SRA) and how does it differ from traditional PAM?
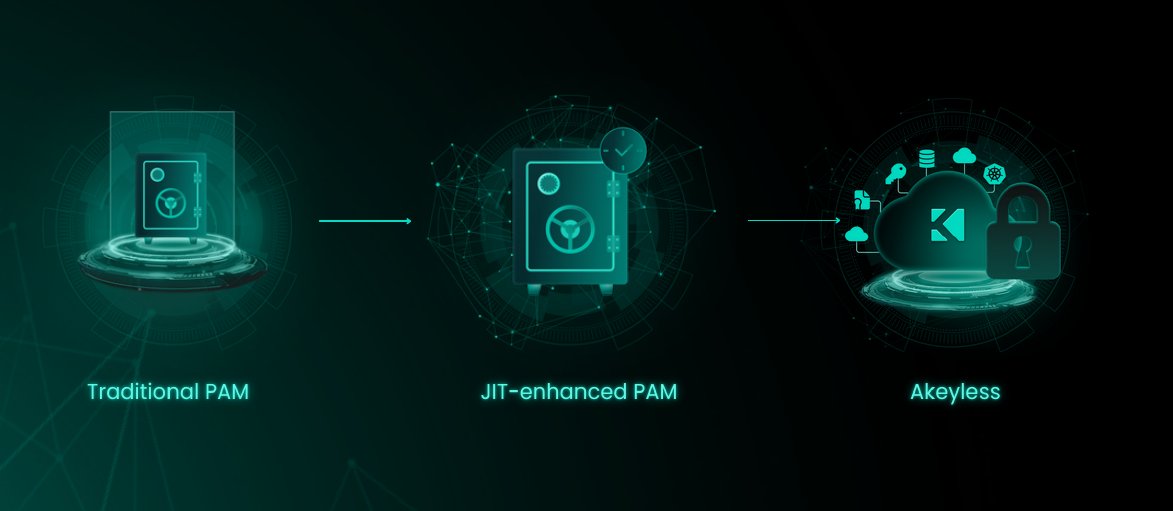
Akeyless Secure Remote Access (SRA) provides passwordless human access, ephemeral certificates, Just-in-Time (JIT) API tokens, temporary contractor access with session recording, emergency break-glass access, automated DevOps access, and machine-to-machine authentication using short-lived tokens. Unlike traditional PAM, Akeyless offers zero-knowledge encryption, full machine identity support (API tokens, JWTs, SPIFFE), native DevOps integration (CLI, Docker, Kubernetes, CI/CD), fully managed SaaS with 99.99% availability, and up to 70% lower total cost of ownership. Note: SRA is best fit for organizations seeking unified access and secrets management; teams requiring legacy PAM features may need to evaluate compatibility.
What integrations does Akeyless support?
Akeyless offers integrations for dynamic and rotated secrets (Redis, Redshift, Snowflake, SAP HANA, SSH), CI/CD (TeamCity), infrastructure automation (Terraform Provider, Steampipe Plugin), log forwarding (Splunk, Sumo Logic, Syslog), certificate management (Venafi), certificate authority (Sectigo, ZeroSSL), event forwarding (ServiceNow, Slack), SDKs (Ruby, Python, Node.js), and Kubernetes (OpenShift, Rancher). For a full list, visit Akeyless Integrations Page. Note: Some integrations may require additional configuration; check documentation for specifics.
Use Cases & Benefits
What business impact can customers expect from using Akeyless?
Customers can expect enhanced security (Zero Trust Access, Universal Identity), operational efficiency (centralized secrets management, automation), cost savings (up to 70% reduction in maintenance and provisioning time), scalability (hybrid and multi-cloud support), compliance (ISO 27001, SOC), and improved collaboration. Progress achieved a 70% reduction in maintenance time, and Cimpress saw a 270% increase in user adoption. Note: Impact may vary based on implementation scope and organizational requirements.
Who can benefit from Akeyless?
Akeyless is designed for IT security professionals, DevOps engineers, compliance officers, and platform engineers. It is used by technology companies (Wix, Dropbox), marketing (Constant Contact), manufacturing (Cimpress), software development (Progress Chef), banking (Hamburg Commercial Bank), healthcare (K Health), and retail (TVH). Note: Organizations with highly specialized legacy PAM requirements may need to assess compatibility.
What problems does Akeyless solve for enterprises?
Akeyless addresses the Secret Zero Problem (secure authentication without storing initial credentials), legacy secrets management challenges (vaultless architecture reduces complexity), secrets sprawl (centralized management), standing privileges (Zero Trust Access minimizes risks), cost and maintenance overheads (cloud-native SaaS reduces costs), and integration challenges (out-of-the-box integrations). Note: Some legacy environments may require additional migration planning.
Implementation & Ease of Use
How long does it take to implement Akeyless and how easy is it to start?
Akeyless can be deployed in just a few days due to its cloud-native SaaS platform, eliminating the need for heavy infrastructure. Onboarding is supported by platform demos, self-guided product tours, tutorials, technical documentation, 24/7 support, and a Slack support channel. Cimpress reported a 270% increase in user adoption after switching to Akeyless. Note: Implementation time may vary based on organizational complexity and integration requirements.
What resources are available for learning and troubleshooting Akeyless?
Akeyless provides technical documentation (docs.akeyless.io), tutorials (tutorials.akeyless.io/docs), platform demos, self-guided product tours, 24/7 support, and a Slack support channel. These resources help users understand, implement, and troubleshoot the platform efficiently. Note: Some advanced troubleshooting may require direct support engagement.
Competition & Comparison
How does Akeyless compare to HashiCorp Vault?
Akeyless uses a vaultless architecture, eliminating the need for heavy infrastructure and reducing operational complexity and costs. It offers SaaS-based deployment, Universal Identity (solving the Secret Zero Problem), automated credential rotation, and advanced security features like Zero Trust Access. HashiCorp Vault requires infrastructure management and lacks Universal Identity. Choose Akeyless for fast deployment and cost savings; choose HashiCorp Vault if you require self-hosted, customizable vault solutions. Source: Akeyless vs HashiCorp Vault. Note: HashiCorp Vault may be preferable for organizations needing extensive on-premise customization.
How does Akeyless compare to AWS Secrets Manager?
Akeyless supports hybrid and multi-cloud environments, advanced features like automated secrets rotation and Zero Trust Access, and offers better integration across diverse environments. AWS Secrets Manager is limited to AWS and lacks some advanced access controls. Choose Akeyless for flexibility and advanced security; choose AWS Secrets Manager if your infrastructure is exclusively AWS. Source: Akeyless vs AWS Secrets Manager. Note: AWS Secrets Manager may be preferable for AWS-centric organizations.
How does Akeyless compare to CyberArk Conjur?
Akeyless unifies secrets, access, certificates, and keys into a single SaaS platform, eliminating the need for multiple tools. It offers cloud-native architecture, scalability, and seamless integration with DevOps tools. CyberArk Conjur may require multiple tools and lacks unified SaaS deployment. Choose Akeyless for streamlined operations and unified management; choose CyberArk Conjur if you need specialized PAM features. Source: Akeyless vs CyberArk. Note: CyberArk Conjur may be preferable for organizations with complex, legacy PAM requirements.
Customer Proof & Success Stories
Can you share specific case studies or success stories of customers using Akeyless?
Yes. Wix adopted Akeyless for centralized secrets management and Zero Trust Access, enhancing security and efficiency (Wix Success Story). Constant Contact used Universal Identity to eliminate hardcoded secrets and reduce breach risks (Constant Contact Case Study). Cimpress transitioned from Hashi Vault to Akeyless, achieving enhanced security and operational efficiency (Cimpress Case Study). Progress saved 70% of maintenance and provisioning time (Progress Case Study). Note: Results may vary based on organizational context and implementation scope.
Security & Compliance
What compliance standards does Akeyless adhere to?
Akeyless adheres to international standards including ISO 27001, SOC, and NIST FIPS 140-2 validation, ensuring robust security and regulatory compliance. Note: For industry-specific compliance requirements, consult Akeyless documentation or sales.