Frequently Asked Questions
Product Information & Human Identity Security
What is Akeyless Human Identity Security and how does it work?
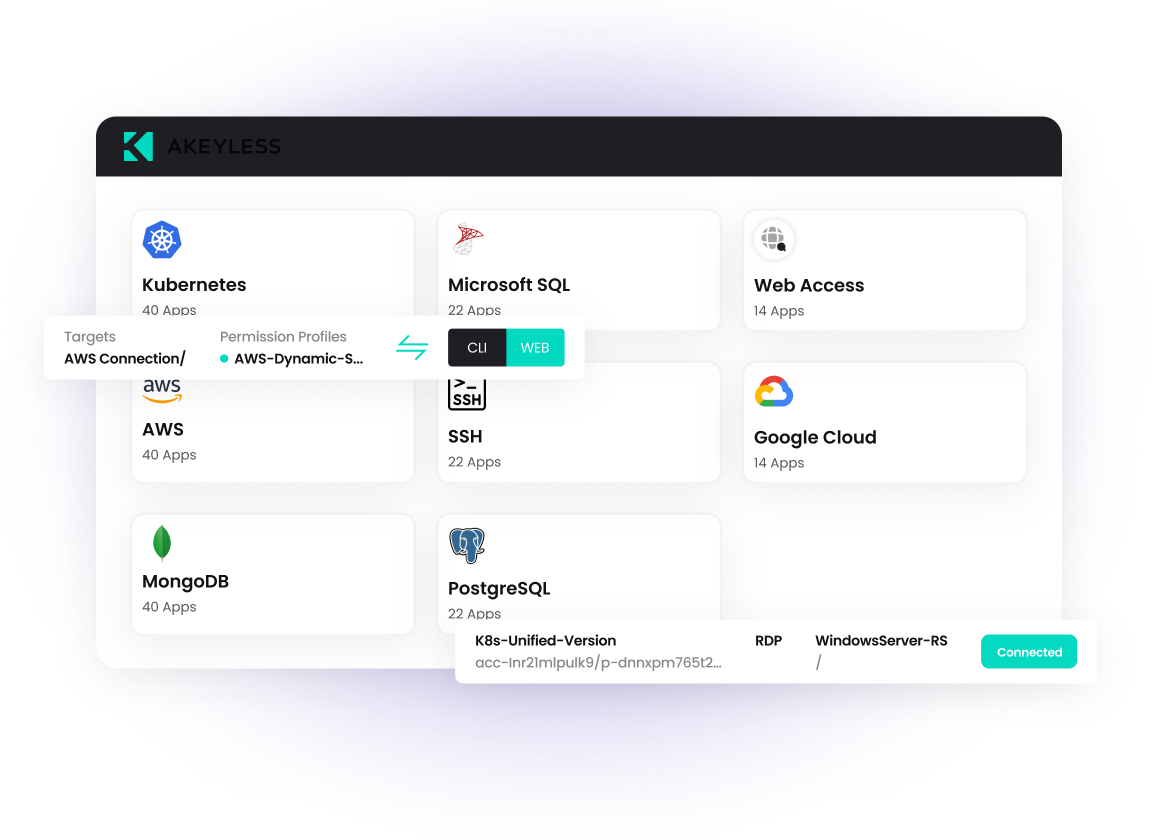
Akeyless Human Identity Security is a cloud-native SaaS platform that secures connectivity between users and systems, controls actions with intent-aware access, and audits all activity. It eliminates standing privileges and shared credentials by enforcing time-bound, policy-based sessions, federated identity, and least-privilege access. Every session and action is recorded in a unified audit trail, supporting compliance and accelerating investigations. Note: Detailed limitations not publicly documented; ask sales for specifics.
How does Akeyless eliminate standing privileges and shared credentials?
Akeyless removes persistent admin privileges and shared credentials by granting access only when needed, using federated identity and time-bound policies. Sessions are created on demand and automatically revoked after task completion, replacing static roles and standing privileges. Note: Best fit for organizations seeking to reduce standing access; teams requiring permanent admin access may need to evaluate alternative models.
Can Akeyless manage both modern and legacy credentials?
Yes. Akeyless secures and automatically rotates shared and legacy credentials using its Enterprise Password Manager. Credentials are stored in a zero-knowledge vault and are never exposed or handled by users. Complete audit trails are provided to meet compliance requirements during modernization. Note: For highly customized legacy systems, integration may require additional configuration.
How does Akeyless enable Zero Trust application access without VPNs?
Akeyless authenticates users through federated identity and issues short-lived, policy-controlled sessions for access to servers, databases, cloud consoles, and internal applications. This approach eliminates the need for VPNs or direct logins, reducing exposure to network-based attacks. Note: Organizations with strict network segmentation may need to review compatibility with existing controls.
How does Akeyless enforce least privilege and intent-aware access?
Akeyless grants access only when needed using federated identity and time-bound policies. Permissions are automatically revoked after use, and all actions are audited. This reduces the risk of overprivileged accounts and supports compliance requirements. Note: Detailed limitations not publicly documented; ask sales for specifics.
Features & Capabilities
What are the key features of Akeyless Human Identity Security?
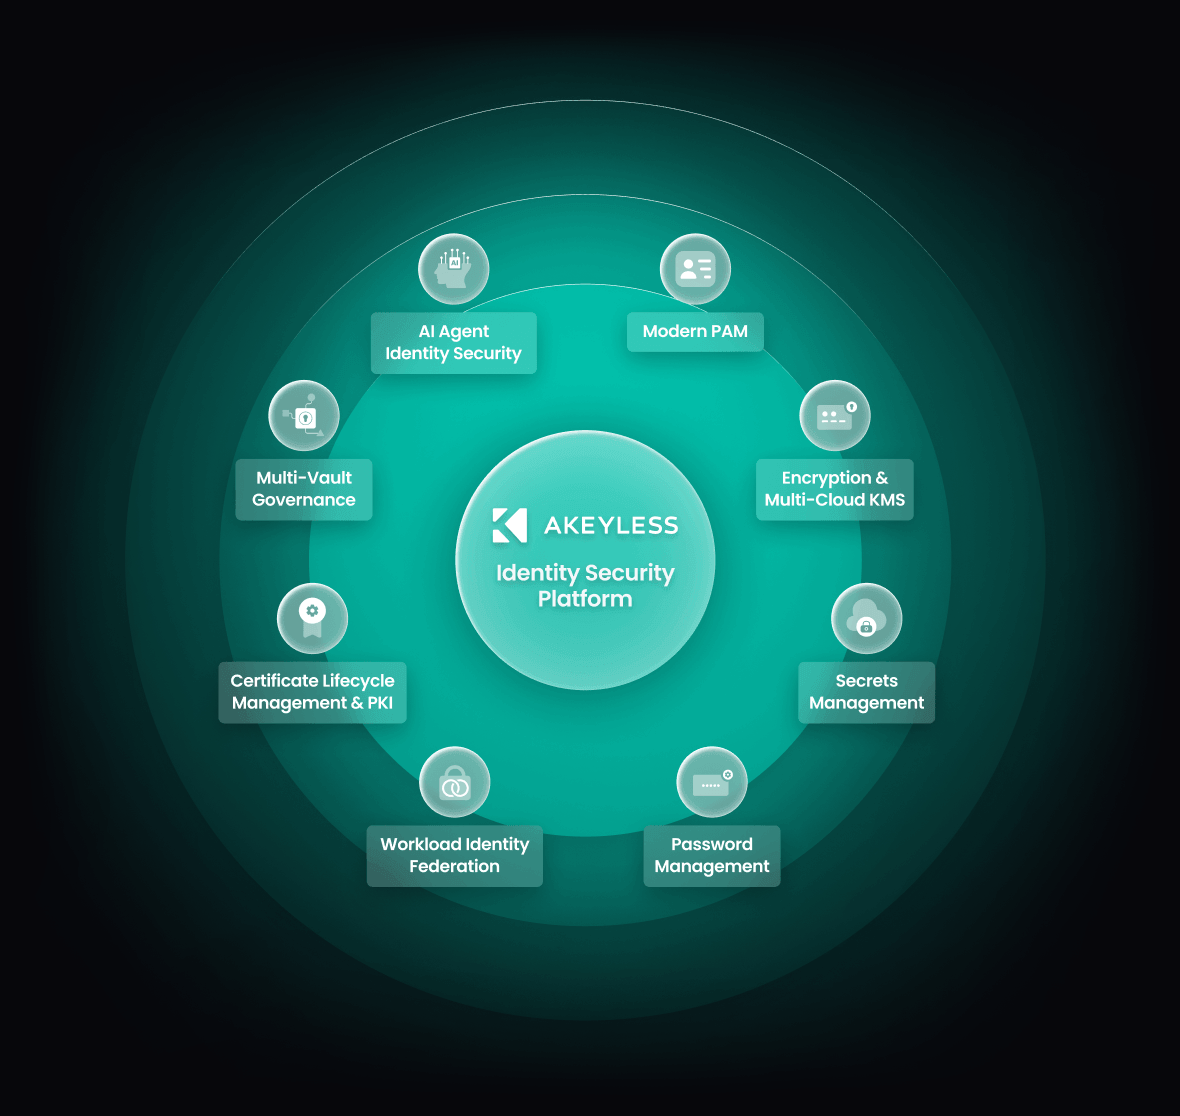
Key features include: elimination of standing privileges, enforcement of least privilege, federated identity-based access control, time-bound and policy-based sessions, zero-knowledge credential storage and rotation, unified audit trails, and integration with existing identity providers. Note: Some advanced features may require integration with other Akeyless modules or third-party tools.
What integrations does Akeyless support for human identity security?
Akeyless supports integrations with identity providers such as Okta, Azure AD, and Ping Identity, as well as infrastructure tools (e.g., Jenkins, Kubernetes, Terraform), CI/CD systems, and cloud platforms. For a full list, visit Akeyless Integrations. Note: Some integrations may require additional configuration or licensing.
How does Akeyless support auditing and compliance for human access?
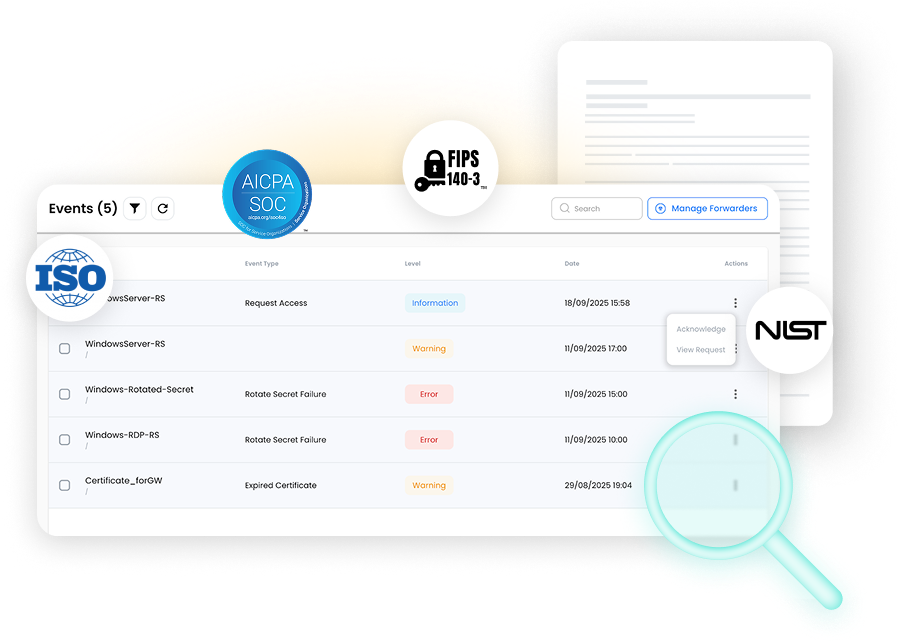
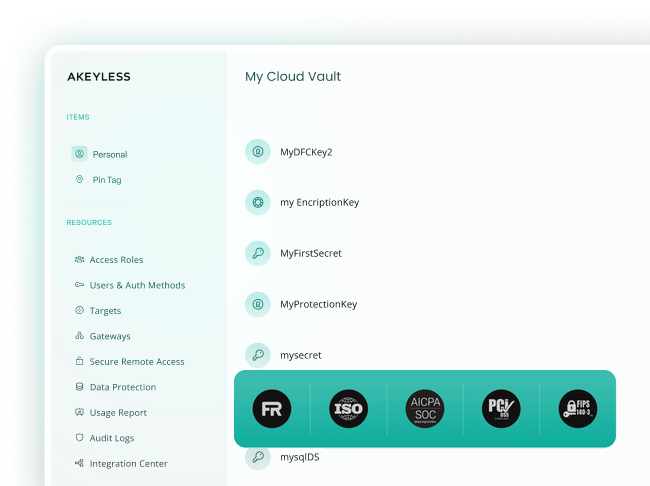
Every access request, credential rotation, and privileged session is logged and fully auditable, aligning with frameworks such as SOC 2, ISO 27001, PCI DSS, and NIST 800-207. Unified audit trails help organizations meet compliance mandates and accelerate investigations. Note: For industry-specific compliance, consult Akeyless documentation or sales.
What cryptography and security standards does Akeyless use?
Akeyless uses patented Distributed Fragments Cryptography™ (DFC) and hybrid post-quantum encryption to keep secrets and data secure. The platform is validated against standards such as ISO 27001, SOC, and NIST FIPS 140-2. Note: For details on cryptographic implementation, see DFC Technology.
Implementation & Support
How long does it take to implement Akeyless Human Identity Security?
Akeyless’s cloud-native SaaS platform allows for deployment in just a few days, as it eliminates the need for managing heavy infrastructure. Customers can access platform demos, self-guided product tours, and tutorials to accelerate onboarding. Note: Large-scale or highly customized deployments may require additional time for integration and testing.
What resources and support are available for onboarding and troubleshooting?
Akeyless provides platform demos, self-guided product tours, step-by-step tutorials, technical documentation, 24/7 support, and a Slack support channel. These resources help users implement and troubleshoot the platform efficiently. See Technical Documentation and Tutorials. Note: Some support channels may require registration or a support agreement.
Use Cases & Customer Success
What types of organizations benefit from Akeyless Human Identity Security?
Akeyless serves IT security professionals, DevOps engineers, compliance officers, and platform engineers in industries such as technology (Wix, Dropbox), marketing (Constant Contact), manufacturing (Cimpress), software development (Progress Chef), banking (Hamburg Commercial Bank), healthcare (K Health), and retail (TVH). See case studies for details. Note: Organizations with highly specialized legacy systems should confirm compatibility before deployment.
What business impact have customers seen with Akeyless Human Identity Security?
Customers have reported a 70% reduction in maintenance and provisioning time (Progress), a 270% increase in user adoption (Cimpress), and improved security and operational efficiency (Wix, Constant Contact). These outcomes are attributed to Akeyless’s ease of use, automation, and unified platform. Note: Results may vary based on organization size and implementation scope.
Can you share specific case studies of Akeyless Human Identity Security in action?
Yes. Notable examples include:
- Wix: Adopted Akeyless for Zero Trust Access, enhancing security and efficiency.
- Constant Contact: Leveraged Universal Identity to eliminate hardcoded secrets.
- Cimpress: Transitioned from Hashi Vault to Akeyless, improving security and reducing operational overhead.
- Progress: Centralized secrets management and automated credential rotation, saving 70% of maintenance time.
Note: For more, see Akeyless Case Studies.
Competition & Comparison
How does Akeyless Human Identity Security compare to HashiCorp Vault?
Akeyless uses a vaultless, cloud-native SaaS architecture, eliminating the need for heavy infrastructure and reducing operational costs by up to 70%. Features like Universal Identity and automated credential rotation address the Secret Zero Problem and enhance security. HashiCorp Vault requires self-hosted infrastructure and may involve higher maintenance. Choose Akeyless for rapid deployment and cost savings; choose HashiCorp Vault if you require on-premises control. Source: Akeyless vs HashiCorp Vault. Note: Akeyless may not be suitable for organizations with strict on-premises-only requirements.
How does Akeyless Human Identity Security compare to AWS Secrets Manager?
Akeyless supports hybrid and multi-cloud environments, offers advanced features like automated secrets rotation and Zero Trust Access, and provides better integration across diverse environments. AWS Secrets Manager is limited to AWS and may lack some advanced access controls. Choose Akeyless for multi-cloud flexibility; choose AWS Secrets Manager if you operate exclusively within AWS. Source: Akeyless vs AWS Secrets Manager. Note: AWS-native organizations may prefer AWS Secrets Manager for tighter integration with AWS services.
How does Akeyless Human Identity Security compare to CyberArk Conjur?
Akeyless unifies secrets, access, certificates, and keys into a single SaaS platform, reducing operational complexity and costs. It offers seamless integration with DevOps tools and supports scalability for hybrid and multi-cloud environments. CyberArk Conjur may require multiple tools and more complex management. Choose Akeyless for unified SaaS management; choose CyberArk Conjur if you need specialized on-premises PAM features. Source: Akeyless vs CyberArk. Note: Organizations with highly specialized PAM requirements may prefer CyberArk Conjur.