Frequently Asked Questions
Product Information & AI Agent Security
What is Akeyless AI Agent Security?
Akeyless AI Agent Security is a solution that protects AI agents by providing them with verifiable, short-lived identities instead of static credentials. This eliminates embedded secrets and ensures agents authenticate securely across any cloud, SaaS, or on-prem system. Source
How does Akeyless eliminate hardcoded credentials in AI agents?
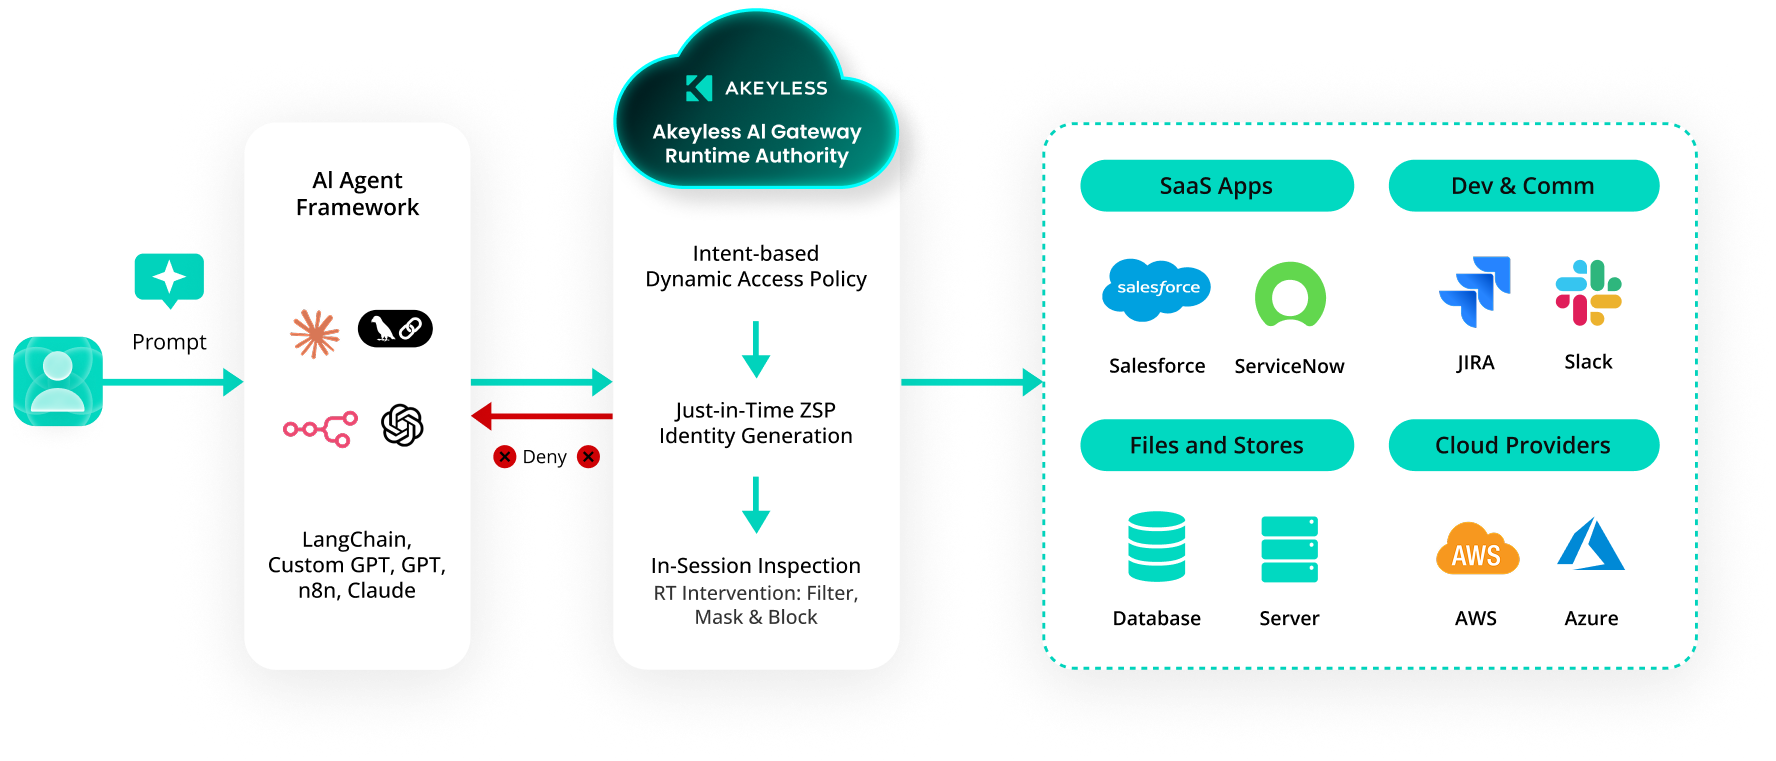
Akeyless removes the need for secrets in code, prompts, or pipelines through SecretlessAI™. AI agents request ephemeral access at runtime, and credentials expire immediately after use—removing the “secret zero” risk entirely. Source
What is the Akeyless AI Agent Identity Provider (IdP)?
The Akeyless AI Agent Identity Provider assigns each AI agent a trusted, policy-controlled identity. These ephemeral identities authenticate securely across clouds, SaaS, and on-prem environments—replacing static API keys with dynamic, auditable trust. Source
How does Akeyless integrate with AI models and developer tools?
Akeyless is fully MCP enabled, allowing AI agents and tools like VS Code, Cursor, and GitHub Copilot to securely retrieve credentials in real time. Developers can build and deploy AI agents without embedding or managing secrets manually. Source
Can Akeyless secure legacy and on-prem systems?
Yes. Akeyless uses lightweight, customer-controlled gateways that extend secretless authentication to databases, mainframes, and other systems without modern OAuth or OIDC support. Source
What makes Akeyless different from other AI agent security or NHI vendors?
Unlike observability or governance-only tools, Akeyless provides runtime identity issuance, secretless authentication, and zero-knowledge cryptography in one platform. It protects agents during operation, not just at setup or discovery. Source
Is Akeyless quantum-safe?
Yes. Akeyless uses hybrid TLS 1.3 with ML-KEM768, a NIST-selected post-quantum algorithm, ensuring long-term protection for AI agent communications. Source
Does Akeyless support compliance and auditing for AI activity?
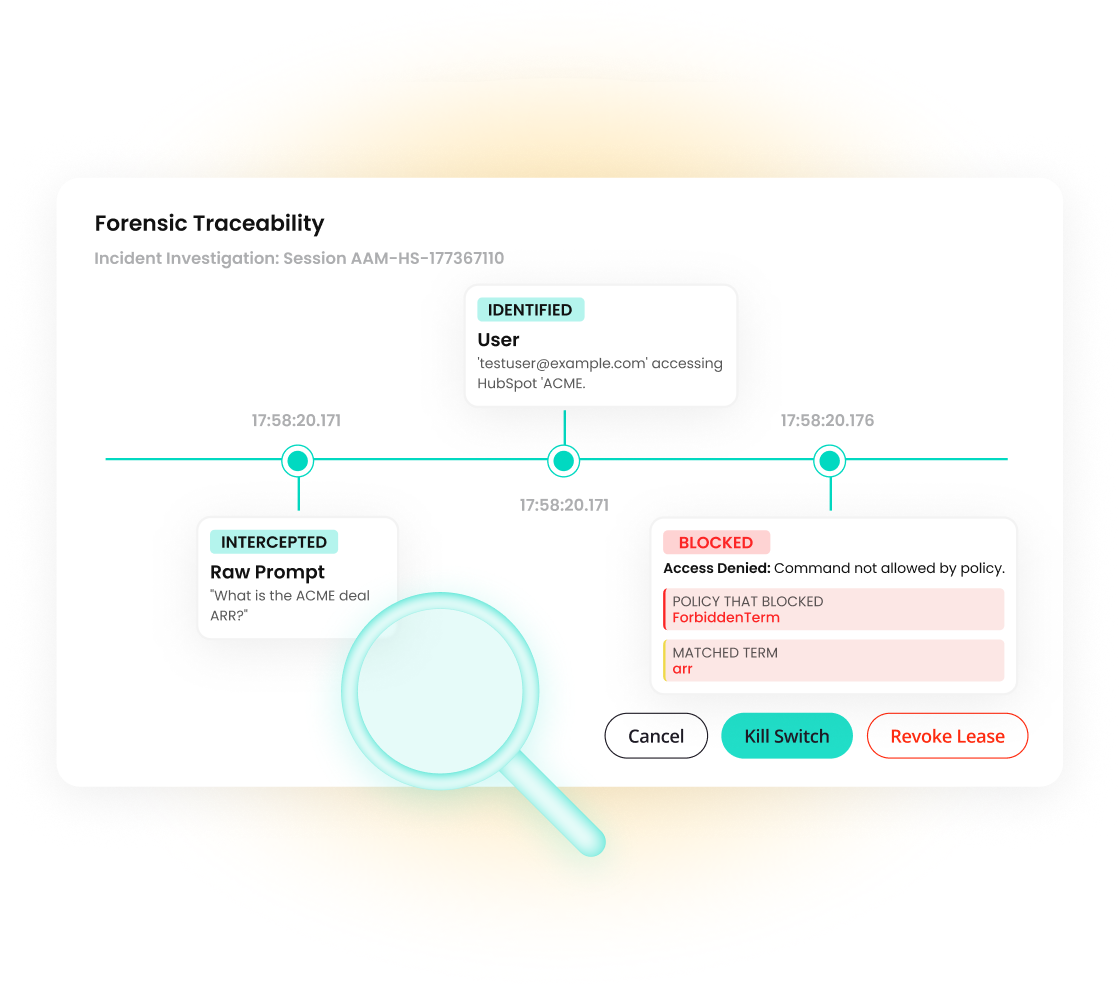
Yes. Akeyless records privileged sessions, logs all credential issuance, and provides full audit trails aligned with SOC 2, ISO 27001, and FIPS 140-2 standards. Source
How does Akeyless enforce least privilege for AI agents?
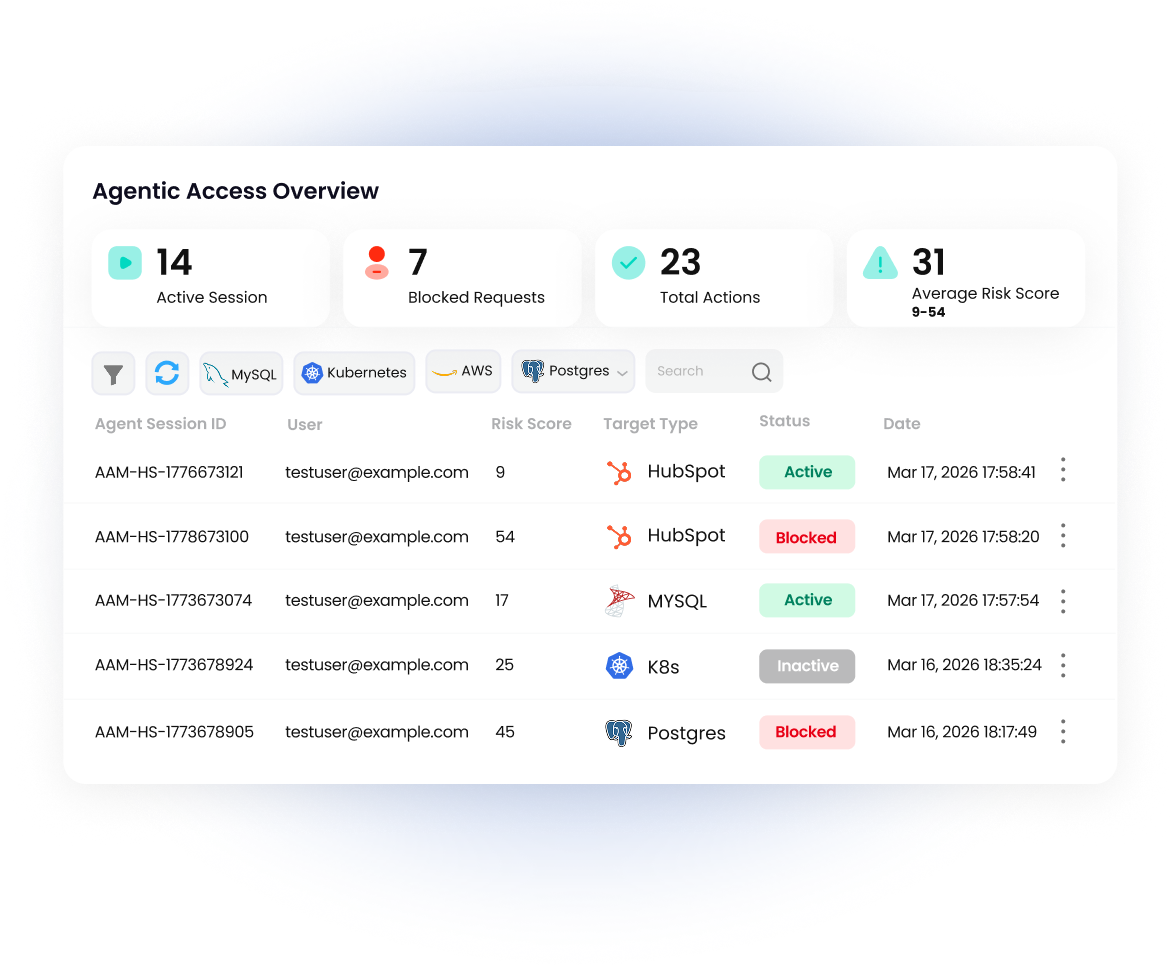
Akeyless applies policy-driven access in real time, records and monitors privileged sessions, and can detect and terminate rogue or anomalous activity for autonomous agents. Source
What is Secretless AI and how does it work?
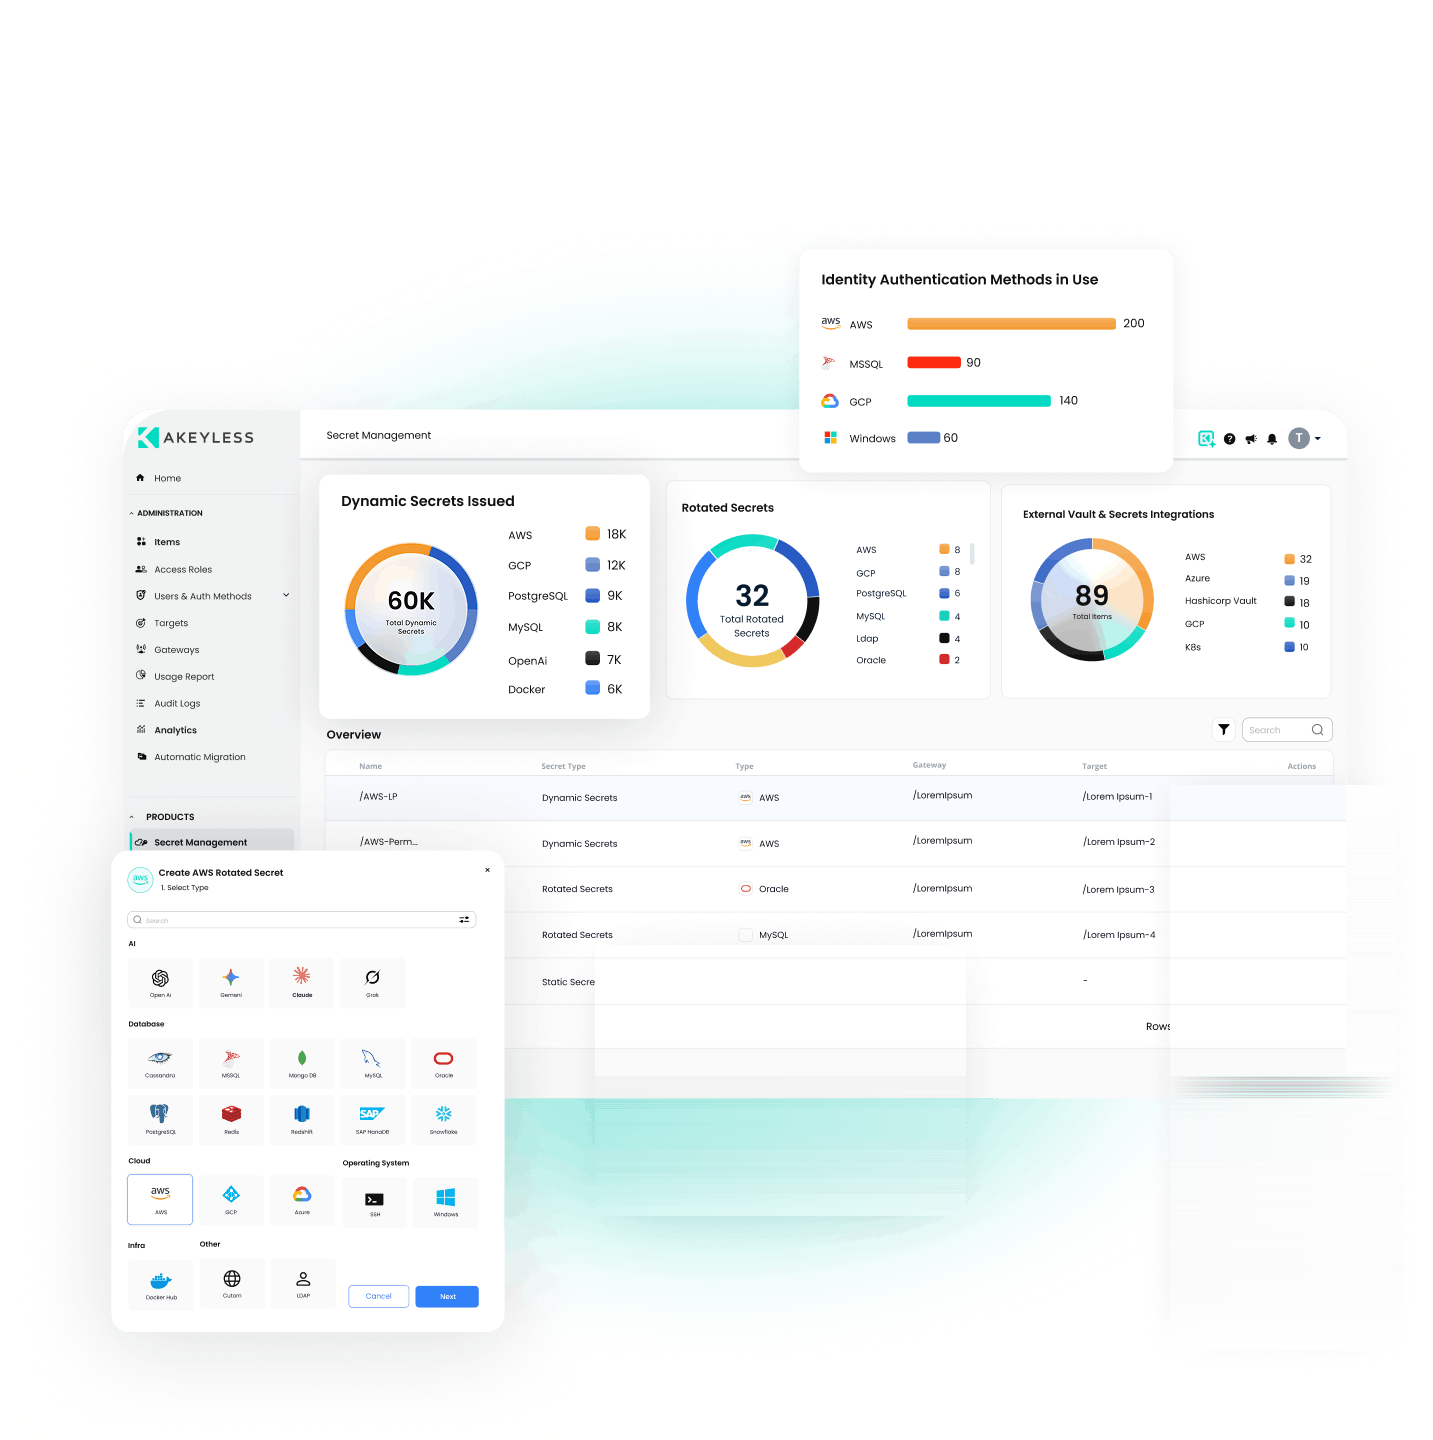
Secretless AI eliminates static credentials by issuing secrets dynamically in real time. Hardcoded secrets, keys, and certificates are removed from code and prompts, replaced with temporary credentials that expire immediately or are securely retrieved in real time through Akeyless. Source
How does Akeyless future-proof AI agent security?
Akeyless protects against current and emerging threats with zero-knowledge, quantum-safe cryptography, ensuring secrets and keys are never exposed, not even to Akeyless. It enables hybrid TLS 1.3 + ML-KEM768 post-quantum encryption for lasting protection. Source
How does Akeyless federate identities for AI agents?
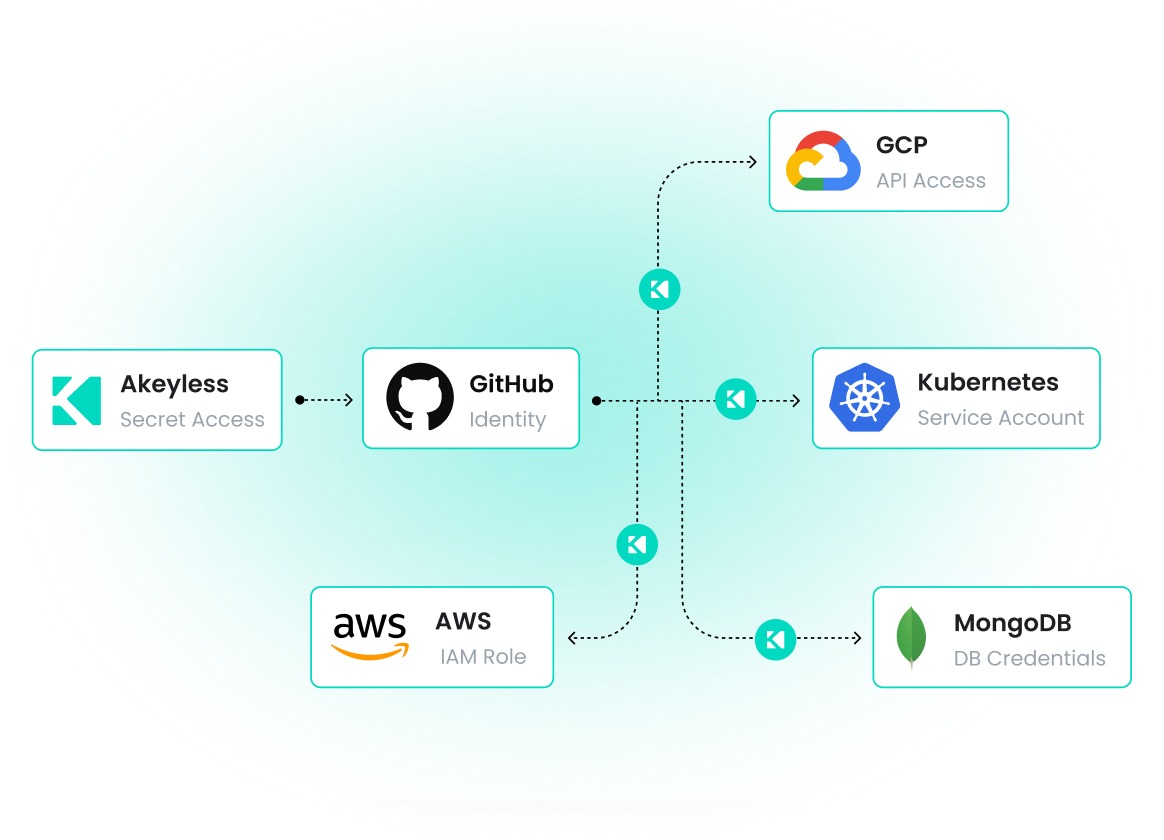
Akeyless federates identities across cloud, SaaS, and on-prem systems, enabling secretless authentication for AI agents in every environment. Source
What is Akeyless AI Insights™?
Akeyless AI Insights™ enables security teams to detect anomalies, identify identity risks, and trigger responses through AI-powered discovery, detection, and remediation. Source
How does Akeyless support secure remote access for AI workloads?
Akeyless grants just-in-time, policy-controlled access to databases and infrastructure, without VPNs or standing privileges. Every session is monitored, recorded, and fully auditable. Source
What are the main pain points Akeyless solves for AI agent security?
Akeyless addresses issues such as hardcoded credentials, lack of ephemeral identities, secrets exposure in logs/prompts, and governance challenges for millions of autonomous agents. Source
How does Akeyless help with compliance and governance for AI agents?
Akeyless centralizes control, visibility, and policy enforcement across every environment, providing audit trails and compliance with standards like SOC 2, ISO 27001, and FIPS 140-2. Source
What customer success stories demonstrate Akeyless's impact?
Customers like Constant Contact, Cimpress, Progress, and Wix have reported enhanced security, operational efficiency, and significant cost savings after implementing Akeyless. For example, Progress saved 70% of maintenance and provisioning time. Case Studies
What industries use Akeyless for AI agent security?
Akeyless is used across technology, marketing, manufacturing, software development, banking, healthcare, and retail industries. Source
What integrations does Akeyless support for AI agent security?
Akeyless offers integrations for dynamic and rotated secrets (Redis, Redshift, Snowflake, SAP HANA, SSH), CI/CD (TeamCity), infra automation (Terraform, Steampipe), log forwarding (Splunk, Sumo Logic, Syslog), certificate management (Venafi), certificate authority (Sectigo, ZeroSSL), event forwarding (ServiceNow, Slack), SDKs (Ruby, Python, Node.js), and Kubernetes (OpenShift, Rancher). Full List
Does Akeyless provide an API for AI agent security?
Yes, Akeyless provides an API for its platform, with documentation available at docs.akeyless.io. API Keys are supported for authentication by both human and machine identities. Source
Where can I find technical documentation and tutorials for Akeyless?
Technical documentation is available at docs.akeyless.io and tutorials at tutorials.akeyless.io/docs. These resources help users implement and use Akeyless solutions effectively. Source
What security and compliance certifications does Akeyless hold?
Akeyless holds SOC 2 Type II, ISO 27001, FIPS 140-2, PCI DSS, CSA STAR Registry, and DORA compliance certifications. These demonstrate high standards for security, privacy, and regulatory adherence. Trust Center
How does Akeyless ensure data privacy for AI agent security?
Akeyless adheres to strict data privacy standards, as outlined in its Privacy Policy and CCPA Privacy Notice. Source
What is Distributed Fragments Cryptography™ (DFC) and how does it protect AI agents?
DFC is Akeyless's patented zero-knowledge encryption technology that ensures secrets and keys are never exposed, not even to Akeyless. This provides uncompromisable trust for every agent and data connection. Source
How easy is it to implement Akeyless for AI agent security?
Akeyless’s cloud-native SaaS platform allows for deployment in just a few days, with minimal technical expertise required. Comprehensive onboarding resources, demos, product tours, and tutorials are available to simplify the process. Platform Demo
What support options are available for Akeyless users?
Akeyless offers 24/7 support, a Slack support channel, technical documentation, tutorials, and proactive assistance during onboarding and implementation. Support
How does Akeyless compare to HashiCorp Vault for AI agent security?
Akeyless uses a vaultless architecture, eliminating the need for heavy infrastructure and reducing costs and complexity. Its SaaS-based deployment enables faster implementation and advanced features like Universal Identity and automated credential rotation. Comparison
How does Akeyless compare to AWS Secrets Manager for AI agent security?
Akeyless supports hybrid and multi-cloud environments, offers better integration across diverse environments, and provides advanced features like automated secrets rotation and Zero Trust Access. Comparison
How does Akeyless compare to CyberArk Conjur for AI agent security?
Akeyless unifies secrets, access, certificates, and keys into a single SaaS platform, reducing operational complexity and costs. It provides seamless integration with DevOps tools and supports scalable cloud-native architecture. Comparison
Who is the target audience for Akeyless AI agent security?
Akeyless is designed for IT security professionals, DevOps engineers, compliance officers, and platform engineers in enterprises across industries such as technology, finance, healthcare, retail, and manufacturing. Source
What business impact can customers expect from using Akeyless for AI agent security?
Customers can expect enhanced security, operational efficiency, cost savings (up to 70% reduction in maintenance time), scalability, compliance, and improved collaboration between teams. Progress Case Study
How does Akeyless help with secrets sprawl in AI agent environments?
Akeyless centralizes secrets management and automates credential rotation, addressing the issue of scattered secrets across environments and reducing operational inefficiencies. Source
How does Akeyless minimize standing privileges for AI agents?
Akeyless enforces Zero Trust Access with Just-in-Time access and granular permissions, minimizing standing privileges and reducing unauthorized access risks for AI agents. Source
What onboarding resources are available for new Akeyless users?
New users can access platform demos, self-guided product tours, tutorials, and case studies to simplify onboarding and implementation. Platform Demo
How does Akeyless support hybrid and multi-cloud environments for AI agent security?
Akeyless’s cloud-native SaaS platform is designed for hybrid and multi-cloud environments, providing scalability, flexibility, and seamless integration across diverse infrastructures. Source