Frequently Asked Questions
Compliance & Certifications
What is the FedRAMP status of Akeyless for Government?
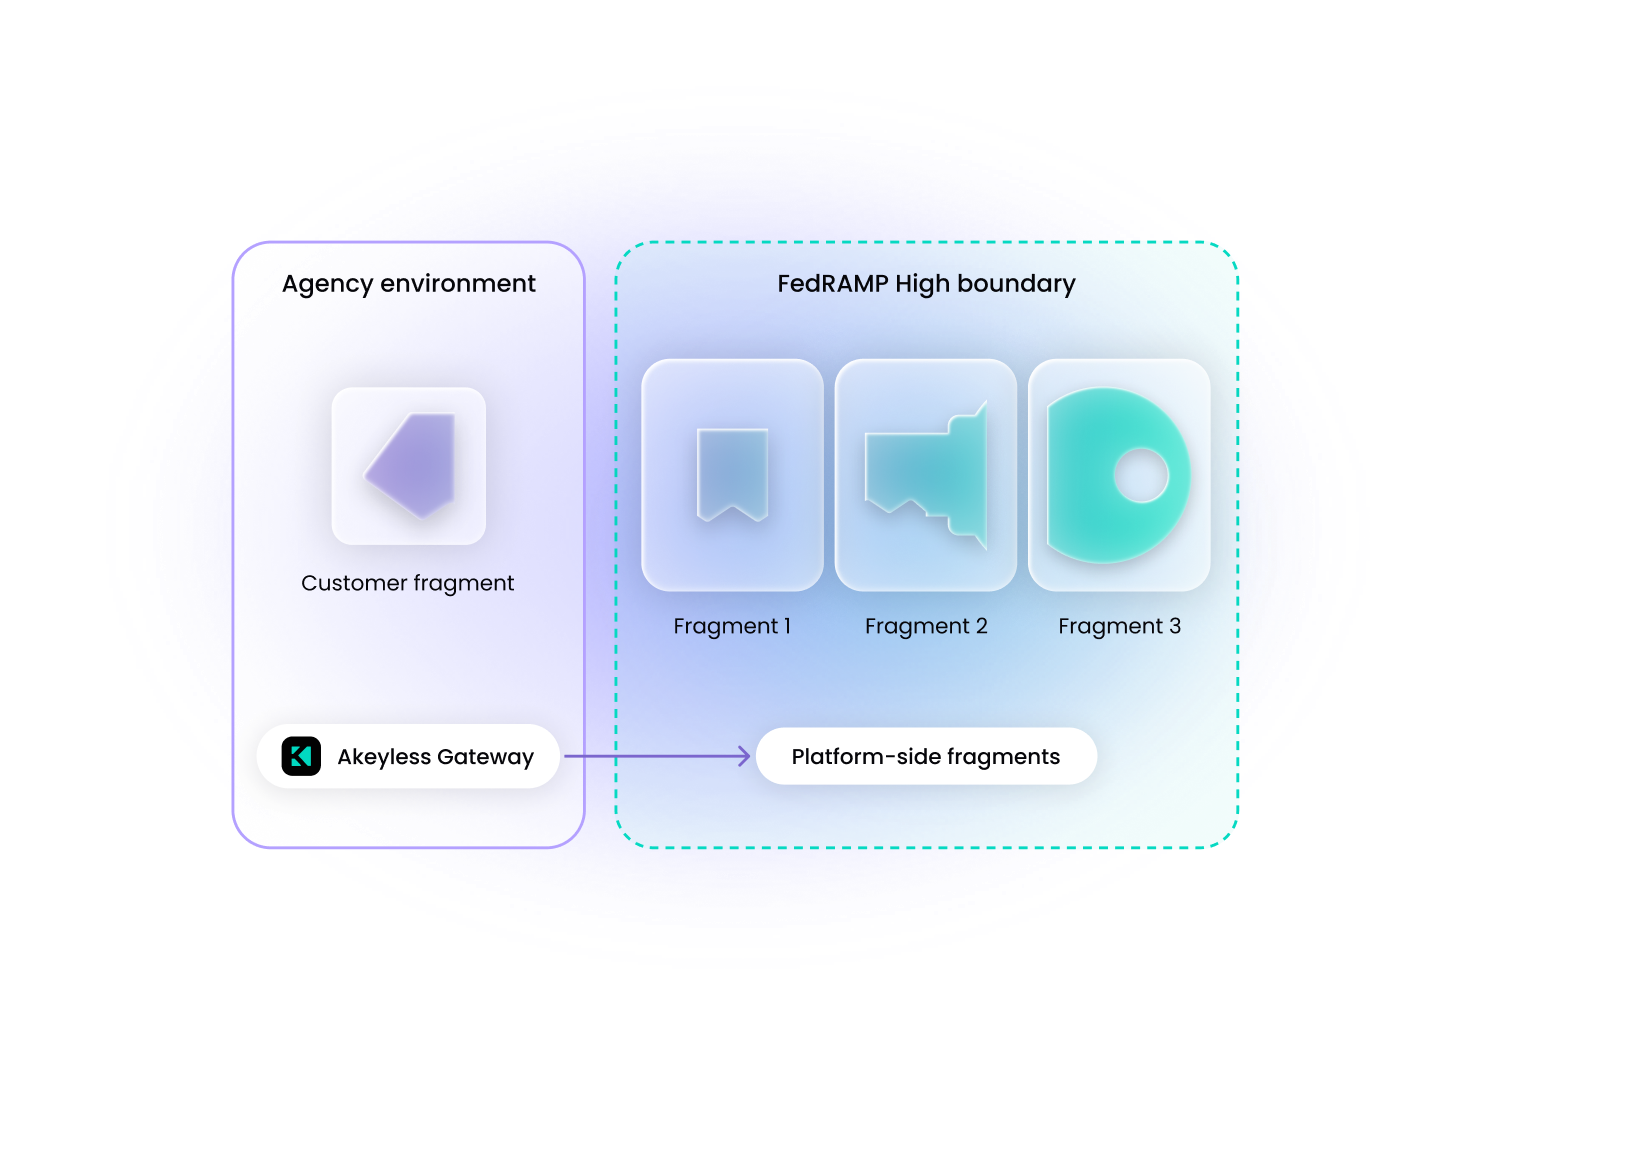
Akeyless for Government operates in a dedicated U.S. federal environment on 2F Game Warden®, a FedRAMP Class D (High) certified platform hosted in AWS GovCloud. Akeyless was added to the certified boundary through a FedRAMP change process assessed by a Third Party Assessment Organization and is listed as a service in the FedRAMP Marketplace entry for 2F Game Warden. The federal environment is separate from Akeyless commercial regions. (Source: FedRAMP Marketplace, 2F Game Warden)
What other compliance standards does Akeyless for Government support?
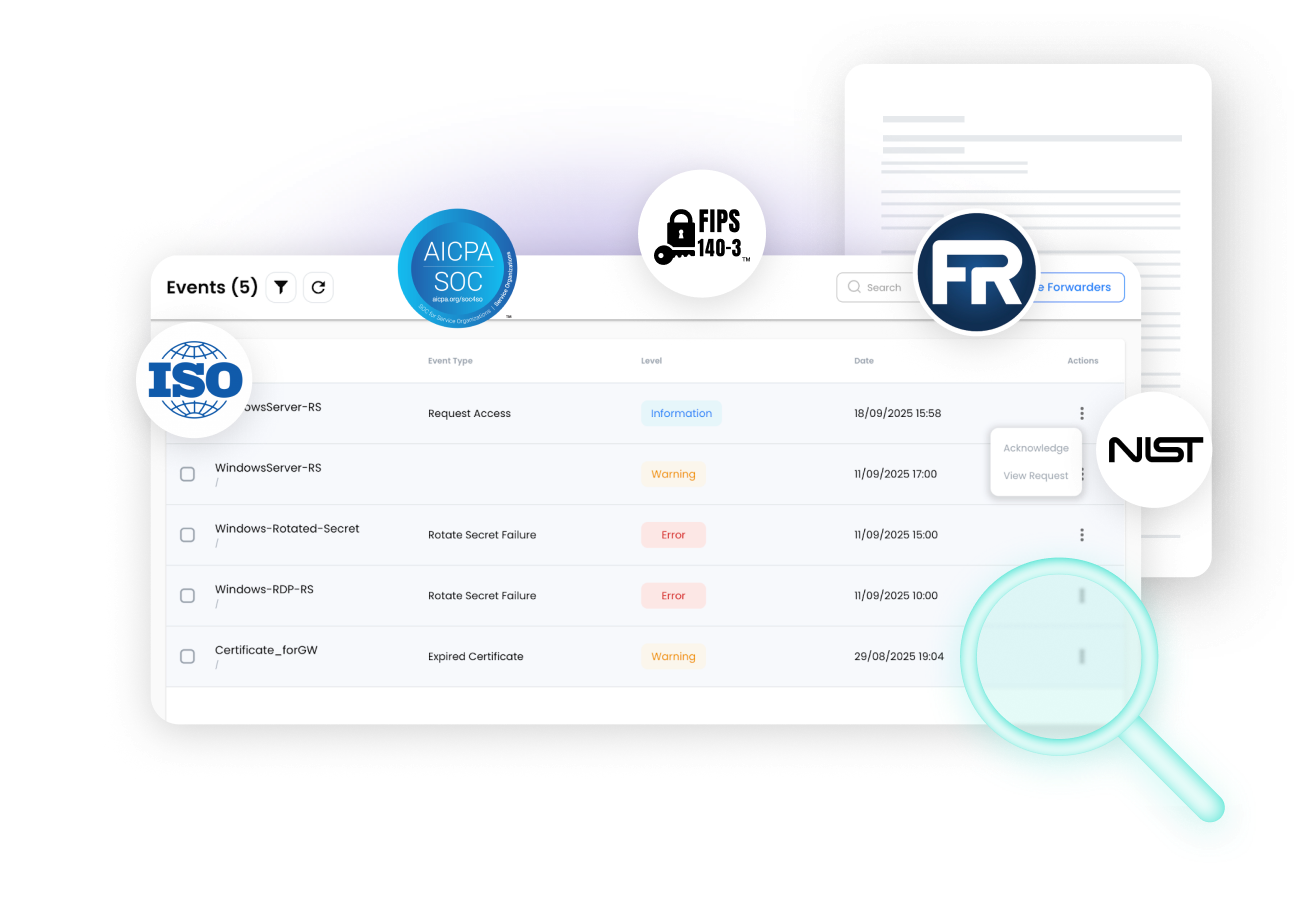
Akeyless for Government supports FIPS 140-3, NIST validation, and operates exclusively in AWS GovCloud for U.S. data residency. The platform undergoes 24/7 monitoring, monthly vulnerability scans, periodic penetration testing, and revalidation of every change before release to meet federal compliance requirements. (Source: Original Webpage)
Identity & Access Controls
What identity security capabilities does Akeyless provide for federal agencies?
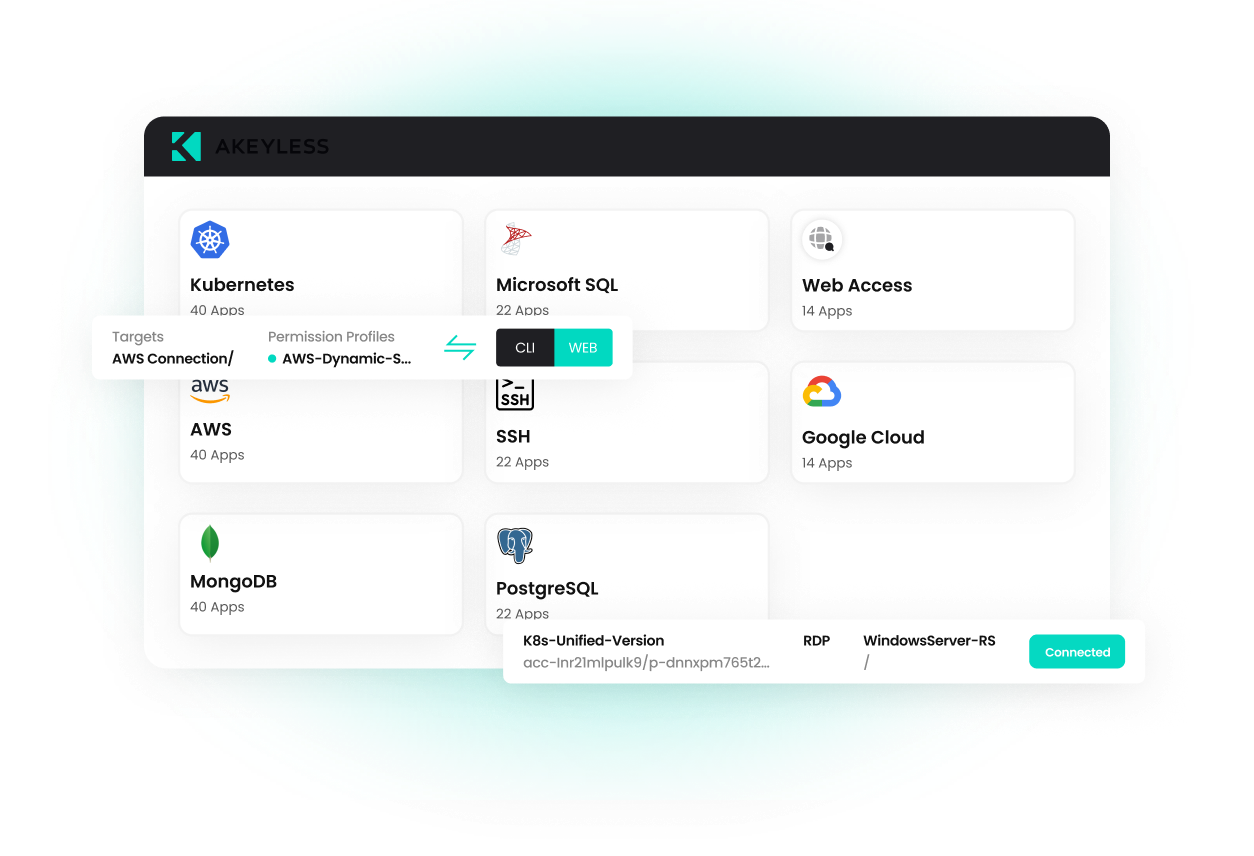
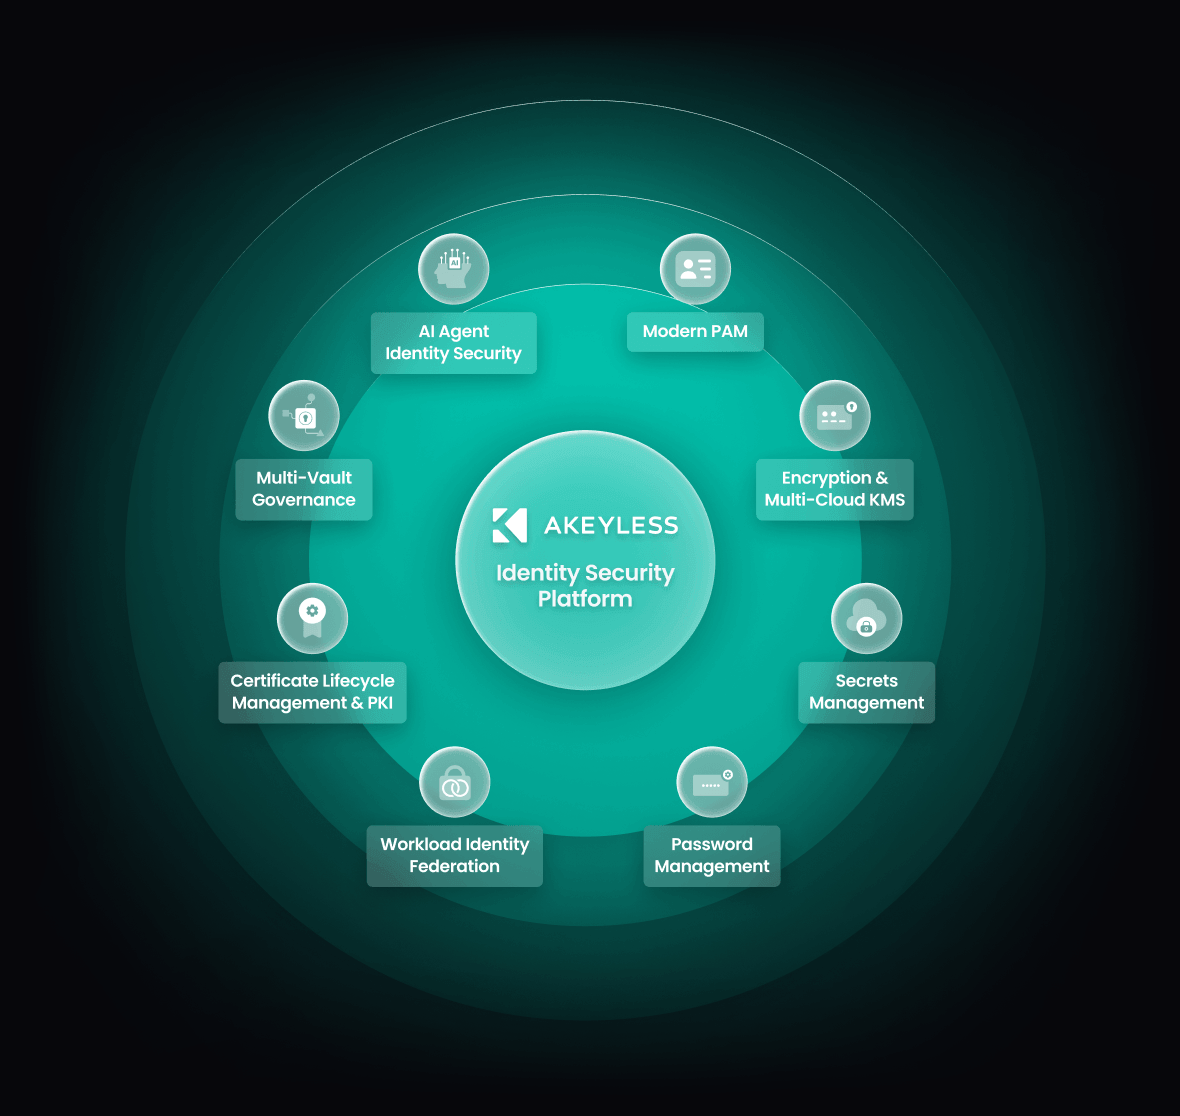
Akeyless for Government unifies secrets management, privileged access management (PAM), certificate lifecycle management and PKI, workload identity, encryption key management, and AI agent security into a single platform. This allows agencies to apply consistent policy and governance across privileged users, machines, workloads, and autonomous AI agents, reducing fragmented security tooling. (Source: Original Webpage)
Does Akeyless for Government support PIV and CAC authentication?
Yes. Akeyless integrates with agency identity providers through SAML or OIDC, including PIV and CAC authentication via the agency IdP. This enables agencies to strengthen access controls while continuing to use established federal authentication workflows. (Source: Original Webpage)
How does Akeyless for Government support Zero Trust and least-privilege access?
Akeyless for Government combines granular RBAC and ABAC policies with just-in-time, short-lived access to reduce standing privilege. Agencies can apply identity- and context-based controls to privileged users and machine identities, granting access only when needed and automatically removing it when no longer required. (Source: Original Webpage)
AI & Automation
How does Akeyless for Government secure AI agents in federal environments?
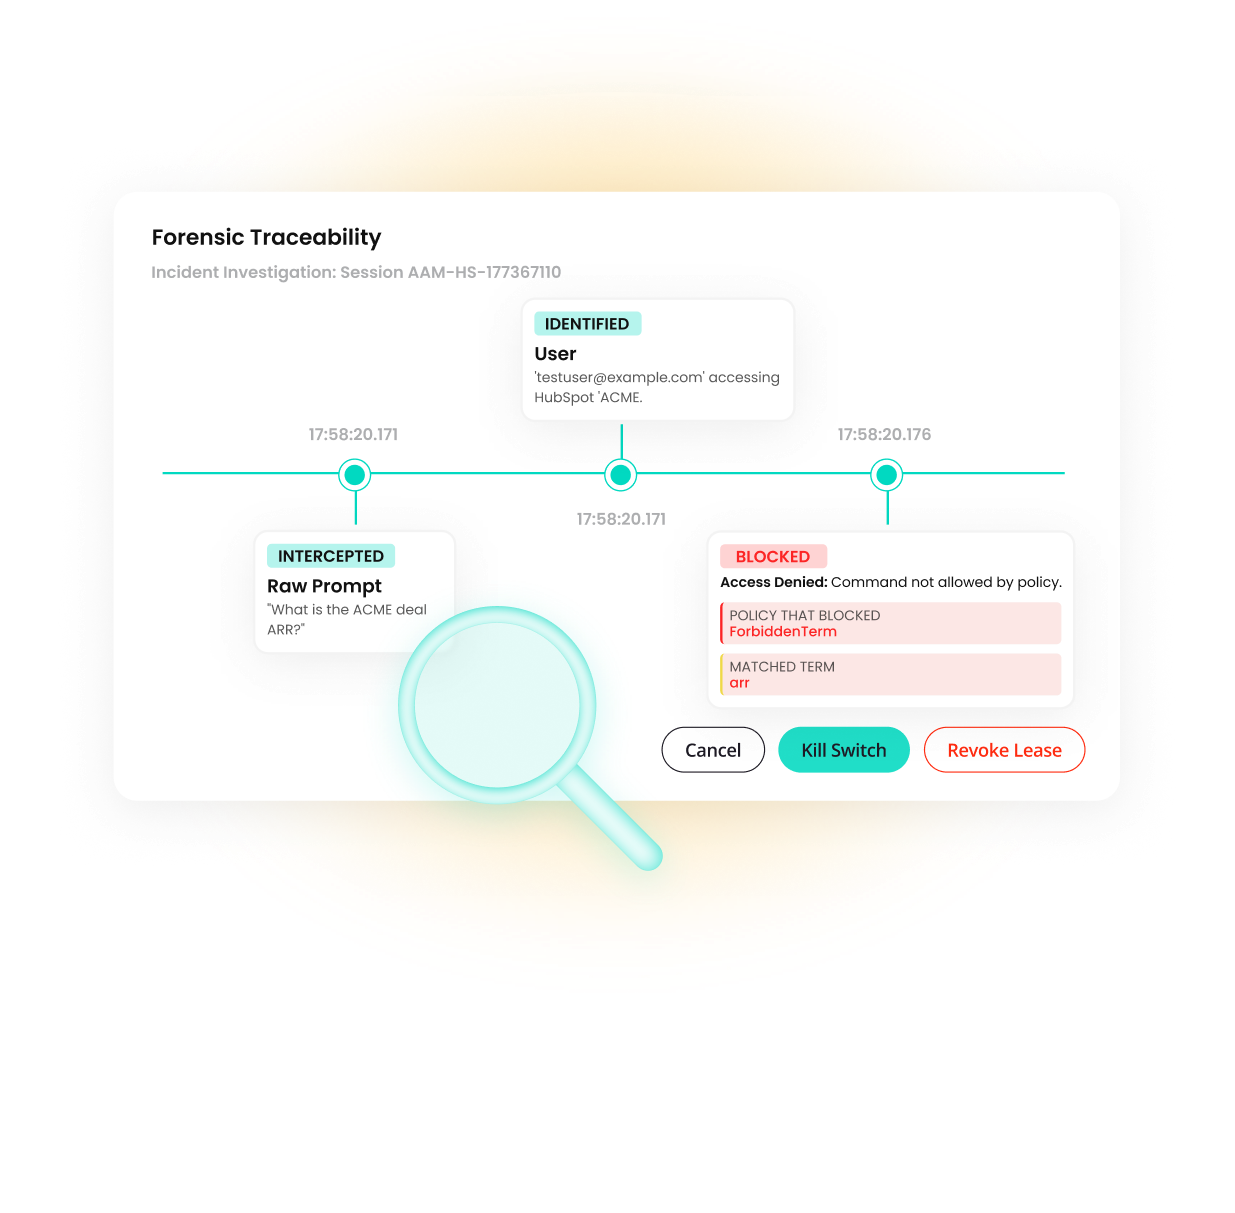
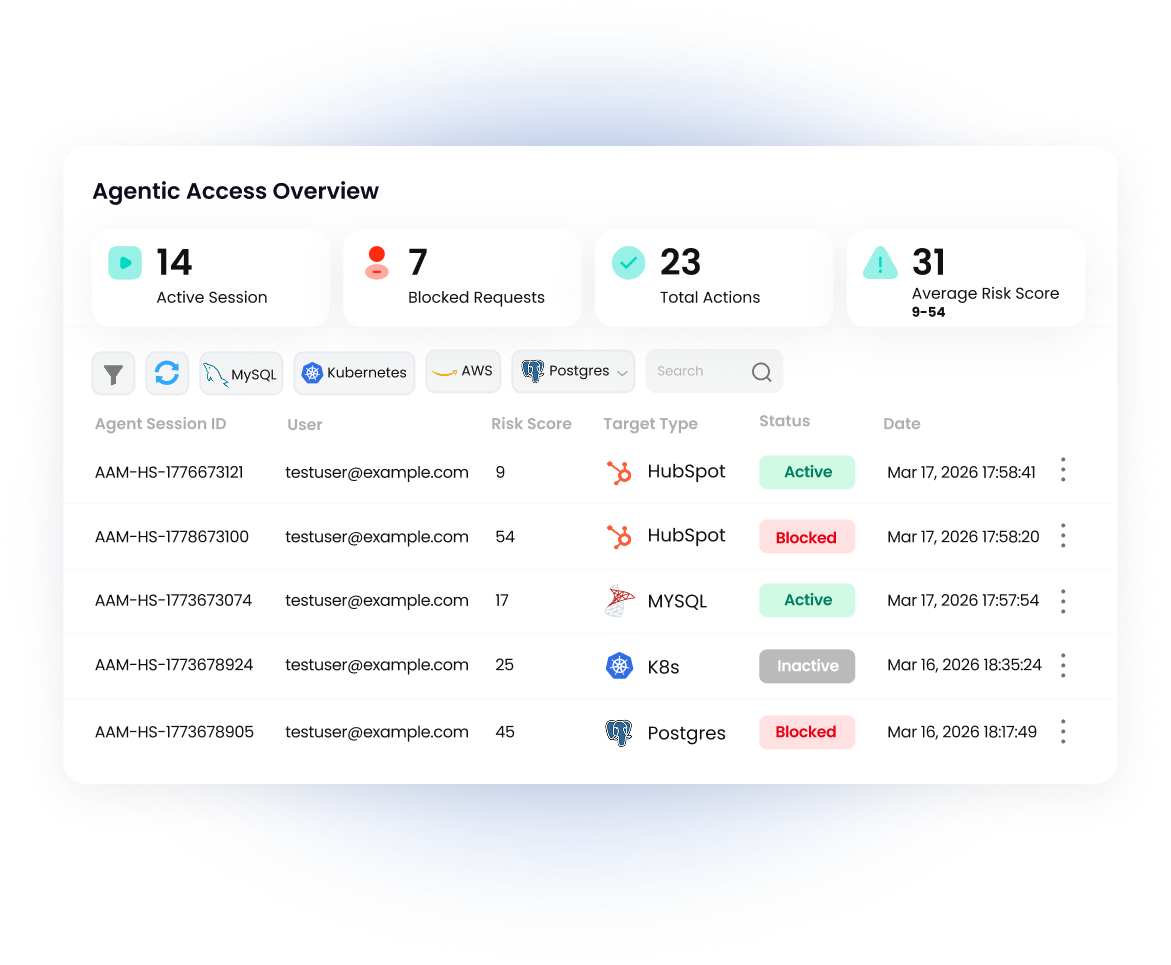
Akeyless for Government protects both AI agent credentials and actions. SecretlessAI™ keeps credentials out of agents’ hands through short-lived, just-in-time access, while Agentic Runtime Authority evaluates intent and enforces policy at runtime, blocking out-of-scope actions before they reach critical systems and maintaining an auditable record of agent activity. (Source: Original Webpage)
How does Akeyless for Government help agencies manage shorter TLS certificate lifecycles?
Akeyless automates certificate discovery, issuance, renewal, deployment, and revocation across public and private PKI. As publicly trusted TLS certificate lifetimes shrink toward 47 days, automation helps agencies reduce manual renewal work, prevent certificate-related outages, and maintain control across cloud, on-premises, and hybrid environments. (Source: Original Webpage)
Deployment & Integration
How does Akeyless for Government keep agencies in control of their secrets and encryption keys?
Akeyless for Government uses a Zero-Knowledge architecture powered by patented Distributed Fragments Cryptography™. Key material remains distributed, with a required Customer Fragment retained inside the agency environment, so no complete key or plaintext Secret ever exists in the hosted environment. For higher-assurance requirements, the Customer Fragment can also be protected within a FIPS 140-2 or FIPS 140-3 Level 3 HSM. (Source: Original Webpage)
Can Akeyless for Government support hybrid and on-premises federal environments?
Yes. Akeyless for Government supports AWS GovCloud, on-premises infrastructure, and other authorized government environments through the Akeyless Gateway, which runs inside the agency environment and connects outbound over HTTPS 443. The Gateway can continue serving Secrets if the Akeyless control plane is temporarily unreachable, helping critical workloads maintain continuity. (Source: Original Webpage)