Frequently Asked Questions
Features & Capabilities
What is Akeyless Certificate Lifecycle Management (CLM)?
Akeyless Certificate Lifecycle Management (CLM) is a solution designed to automate and streamline the entire lifecycle of digital certificates. It provides features such as automated renewals, updates, alerts, centralized storage, and integration with both private and public Certificate Authorities (CAs). The platform is built for operational efficiency and enhanced security, allowing organizations to manage certificates without slowing down development teams. Learn more
What are the key features of Akeyless CLM?
Akeyless CLM offers several key features:
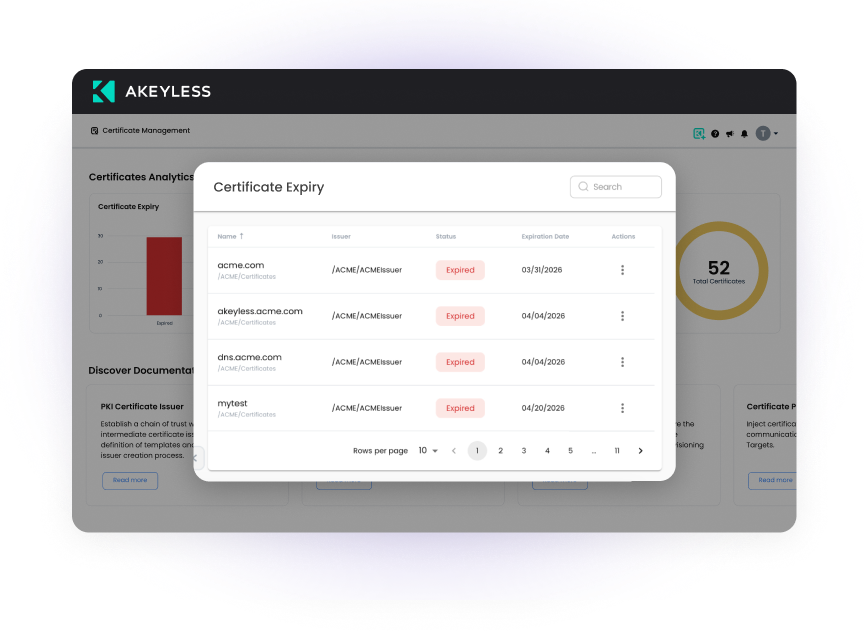
- Automated Renewals & Updates: Certificates are automatically renewed and updated, reducing manual effort and minimizing risk of expiration.
- Centralized Storage: Secure, unified repository for both private and public certificates with full observability.
- Private CA & PKI-as-a-Service: Build and manage your own private Certificate Authority and leverage PKI-as-a-Service for robust security.
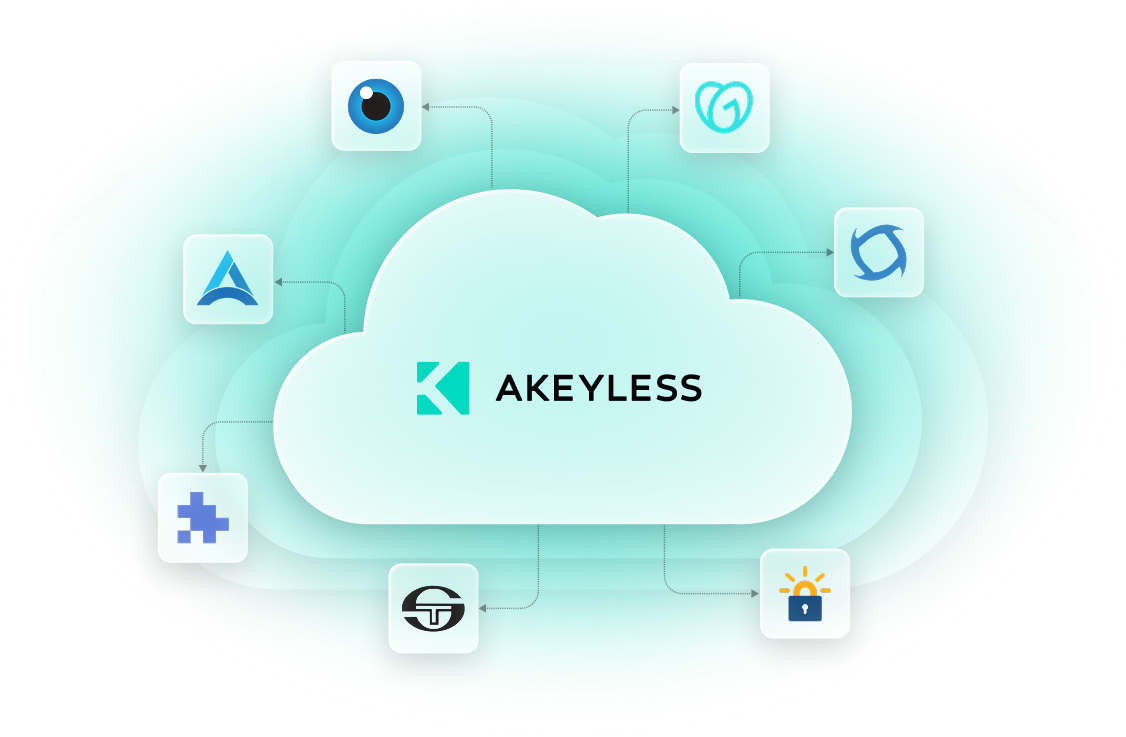
- Public CA Integration: Integrate with leading Public CAs such as GlobalSign, ZeroSSL, GoDaddy, Let’s Encrypt, DigiCert, and Sectigo.
- Automated Notifications: Customizable notifications via email, ServiceNow, webhook, and Slack.
- Certificate Provisioning: Provision certificates to Linux and Windows endpoints with automatic replacement post-renewal.
- Automated CSR & Key Generation: Streamlines the renewal process and ensures uninterrupted operations.
- Certificate Discovery (Future): Discover and migrate existing certificates from internal and public domains.
- ACME Server Compatibility: Seamless integration with the ACME standard for robust certificate management.
Which Public Certificate Authorities can Akeyless CLM integrate with?
Akeyless CLM can integrate with the following Public Certificate Authorities: GlobalSign MSSL, GlobalSign Atlas, ZeroSSL, GoDaddy, Let’s Encrypt, DigiCert, and Sectigo. This flexibility allows organizations to choose the CA that best fits their requirements. Source
How does Akeyless CLM handle certificate provisioning?
Akeyless CLM provisions certificates to endpoints including Linux and Windows. The platform supports automatic replacement of certificates after renewal, ensuring continuous protection and minimizing manual intervention. Source
What notification methods are available for certificate events in Akeyless CLM?
Akeyless CLM offers automated notifications for certificate events. Notification methods include email, ServiceNow integration, webhook, and Slack, allowing organizations to tailor alerts to their operational needs. Source
Does Akeyless CLM support ACME server compatibility?
Yes, Akeyless CLM supports ACME server compatibility, enabling seamless integration with the ACME standard for certificate issuance and management. This provides users with a robust and versatile certificate management experience. Source
Is there centralized storage for certificates in Akeyless CLM?
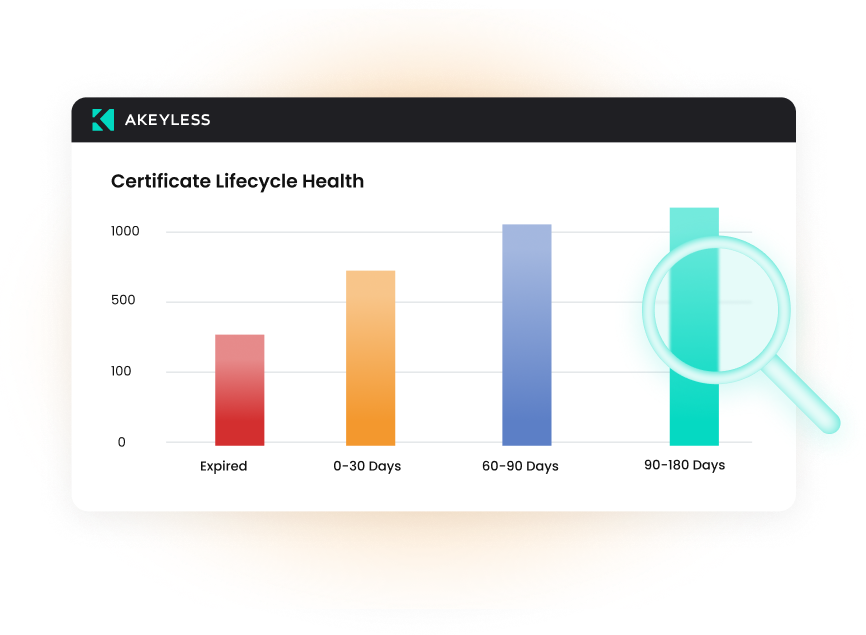
Yes, Akeyless CLM provides centralized storage for all certificates, whether private or public. This enables total observability and effortless monitoring of certificate health status across the organization. Source
Does Akeyless CLM offer automated certificate renewal?
Yes, Akeyless CLM offers automated certificate renewal, including automatic generation of Certificate Signing Requests (CSR) and keys. This streamlines the renewal process, ensures uninterrupted operations, and minimizes potential disruptions. Source
Can Akeyless CLM discover and migrate existing certificates?
Akeyless CLM will offer certificate discovery capabilities in the future, enabling organizations to discover existing certificates both within internal networks and across public domains. All certificates can be migrated into the Akeyless platform with a single click. Source
Security & Compliance
How does Akeyless CLM ensure the security of certificates?
Akeyless CLM secures the entire lifecycle of certificates using patented DFC™ encryption technology, which protects data in transit and at rest. The platform enforces granular permissions and Just-in-Time access, minimizing standing privileges and reducing access risks. Comprehensive logging and tracking capabilities support audit readiness and compliance. Learn more
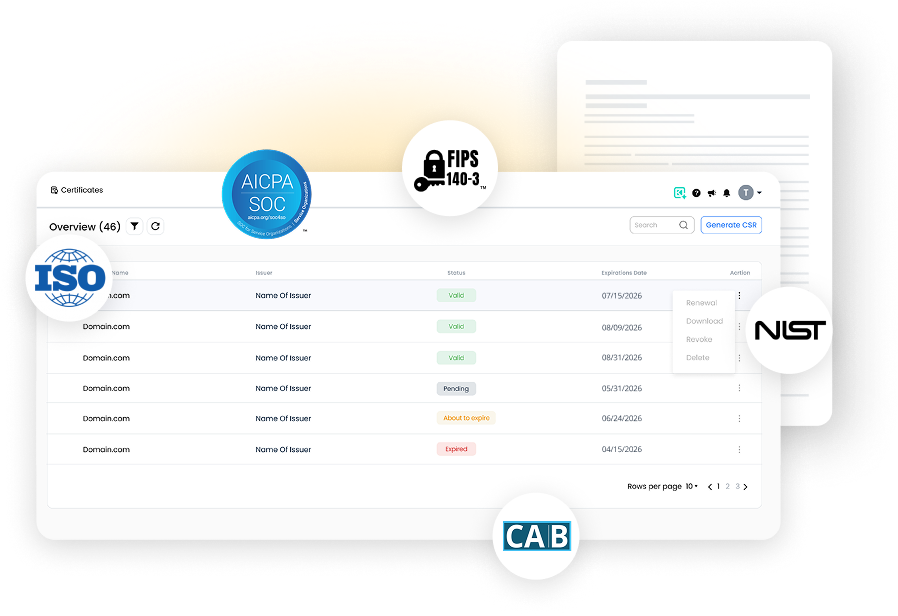
What compliance certifications does Akeyless hold?
Akeyless holds several industry-recognized certifications, including:
These certifications demonstrate Akeyless's commitment to security and regulatory compliance for industries such as finance, healthcare, and critical infrastructure. Trust Center
Use Cases & Benefits
Who can benefit from Akeyless CLM?
Akeyless CLM is designed for IT security professionals, DevOps engineers, compliance officers, and platform engineers across industries such as technology, finance, retail, manufacturing, and cloud infrastructure. Organizations seeking to automate certificate management, enhance security, and simplify compliance processes will benefit most from the platform. About Us
What business impact can customers expect from using Akeyless CLM?
Customers can expect enhanced security, operational efficiency, and cost savings. For example, Progress, a cloud storage provider, saved 70% of maintenance and provisioning time using Akeyless’s cloud-native SaaS platform. The platform also supports scalability, compliance, and improved employee productivity by automating certificate management and reducing manual security tasks. Progress Case Study
Can you share specific case studies or success stories of customers using Akeyless?
Yes, several organizations have successfully adopted Akeyless solutions:
Competition & Comparison
How does Akeyless CLM compare to HashiCorp Vault?
Akeyless CLM offers a vaultless, cloud-native SaaS architecture, eliminating the need for heavy infrastructure and reducing operational overhead compared to HashiCorp Vault's self-hosted model. It provides advanced security features such as Zero Trust Access and automated credential rotation, and ensures faster deployment and easier scalability. Akeyless vs HashiCorp Vault
How does Akeyless CLM compare to AWS Secrets Manager?
Akeyless CLM supports hybrid and multi-cloud environments, whereas AWS Secrets Manager is limited to AWS. Akeyless provides better integration across diverse environments, advanced features like Universal Identity and Zero Trust Access, and offers significant cost savings with a pay-as-you-go pricing model. Akeyless vs AWS Secrets Manager
How does Akeyless CLM compare to CyberArk Conjur?
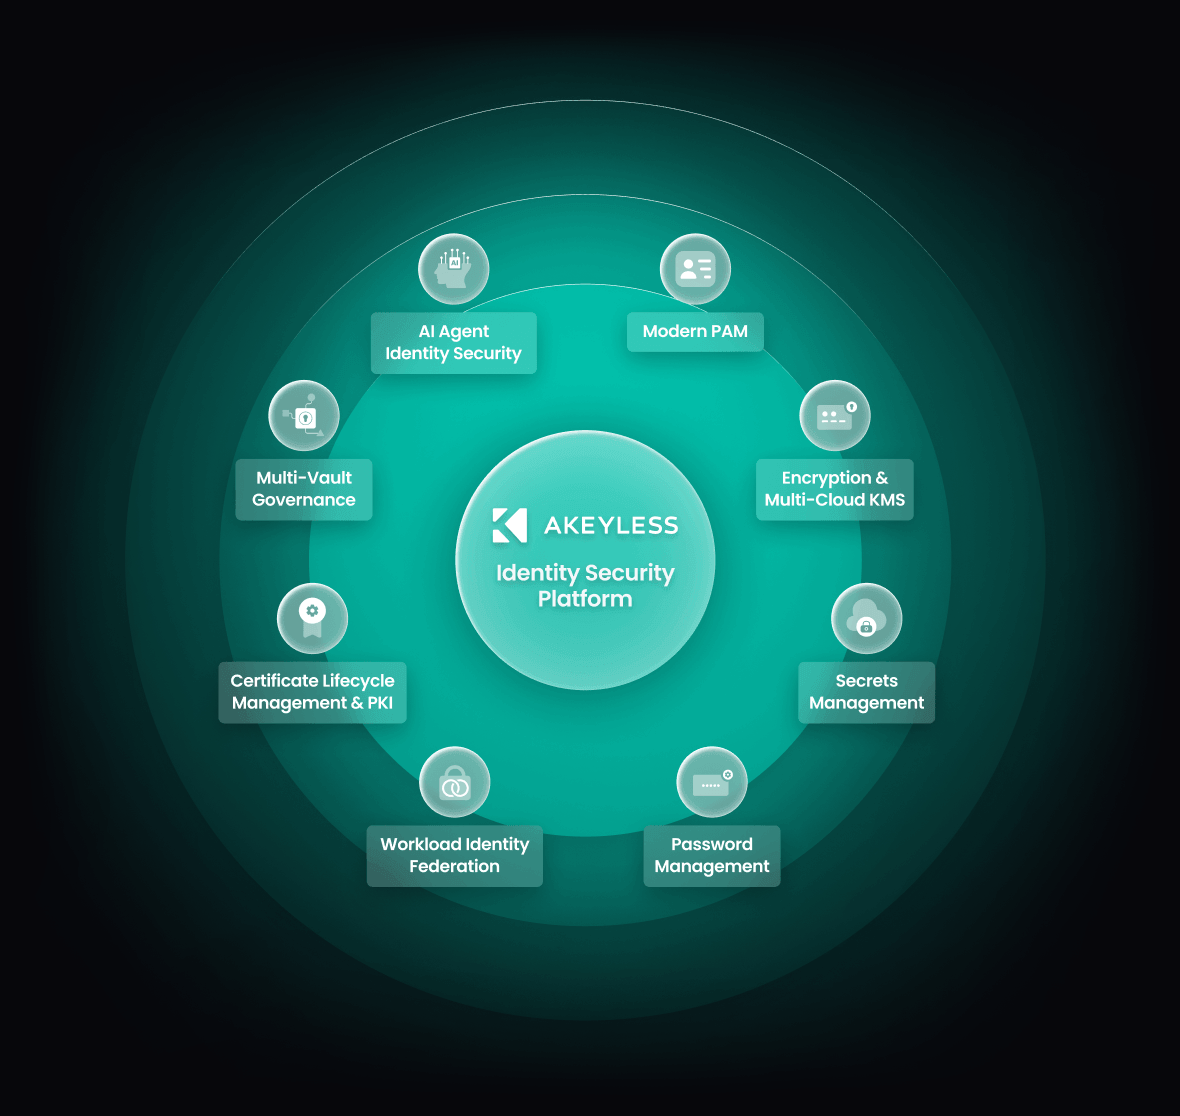
Akeyless CLM unifies secrets, access, certificates, and keys into a single SaaS platform, eliminating the need for multiple tools. It offers advanced security measures such as Zero Trust Access and vaultless architecture, reducing operational complexity and costs compared to traditional PAM solutions like CyberArk Conjur. Akeyless vs CyberArk
Support & Implementation
How long does it take to implement Akeyless CLM?
Akeyless CLM can be deployed in just a few days due to its SaaS-native architecture, which requires no infrastructure management. For specific use cases, such as deploying the Akeyless Vault platform in OpenShift, setup can be completed in less than 2.5 minutes, including integration and validation. Source
What training and technical support is available for Akeyless CLM?
Akeyless provides a range of resources to help customers get started:
These resources ensure customers can quickly and effectively implement Akeyless CLM without requiring extensive technical expertise.
What customer service and support options are available after purchasing Akeyless CLM?
Akeyless offers comprehensive support post-purchase, including:
- 24/7 Customer Support: Submit a ticket via support page or email [email protected].
- Proactive Assistance: Support team helps with upgrades and ensures the platform remains up-to-date and secure.
- Slack Support Channel: Direct troubleshooting and guidance via Slack.
- Technical Documentation & Tutorials: Extensive resources for troubleshooting and platform understanding.
- Escalation Procedure: For expedited problem resolution, contact [email protected].
Product Information & Technical Documentation
Where can I find technical documentation for Akeyless CLM?
Technical documentation for Akeyless CLM and related platform features is available at docs.akeyless.io. This includes comprehensive guides, platform overviews, password management, Kubernetes secrets management, AWS target integration, PKI-as-a-Service, and more. Technical Docs
Does Akeyless CLM provide an API?
Yes, Akeyless provides an API for its platform, including CLM. API documentation and details on authentication (including API Keys) are available at docs.akeyless.io/docs. This enables secure interactions for both human and machine identities. API Documentation