

Frequently Asked Questions

Threat Landscape & AI-Driven Secret Theft

What did Anthropic’s September 2026 Threat Intelligence Report reveal about AI-driven credential theft?

Anthropic’s September 2026 Threat Intelligence Report documented cyber operations where threat actors used Claude to accelerate reconnaissance, credential abuse, exploitation, and data theft. One operator linked to suspected ShinyHunters affiliates ran a distributed pipeline across 10 AWS EC2 workers, downloading and decompiling 1.8 million Android apps to search for hardcoded credentials, API keys, and authentication tokens. In one case, attackers escalated from a single stolen developer token to full cloud administrative control in roughly three hours. Source: Anthropic Threat Intelligence Report. Note: The report highlights the speed and scale at which AI can industrialize credential theft.

How are attackers using AI tools like Claude to steal credentials?

Attackers combine automated secret discovery with AI-assisted exploitation. Claude is used to understand unfamiliar environments, navigate developer and authentication APIs, create and convert privileged tokens, build bulk-collection tooling, and accelerate reconnaissance and data exfiltration. In documented cases, AI agents performed nearly all credential abuse and data theft autonomously. Note: AI reduces manual effort and increases the speed of exploitation, making timely remediation critical.

Why are hardcoded secrets more dangerous in the era of AI?

Hardcoded secrets have always been risky because they can remain valid long after exposure. AI and automation drastically reduce the effort required to find, validate, and exploit those credentials, shortening the window for defenders to detect and remediate. In recent campaigns, attackers weaponized verified secrets within hours. Note: Organizations relying on static credentials face increased risk due to AI-driven automation.

Features & Capabilities

What is the Akeyless GitHub Scanner and how does it help with secret discovery?

The Akeyless GitHub Scanner is a native scanner that connects to your GitHub organization or enterprise and builds a complete picture of your exposure. It discovers secrets across repositories and Git history, inventories organization members, teams, and GitHub Apps, and evaluates risk posture against security policies. The scanner is read-only by design and never reads secret values, only metadata. Setup requires deploying an Akeyless Gateway (version 5.1.0 or later) with AI Insights, connecting a GitHub Target, and running the scanner from the Akeyless Console. Note: The scanner does not remediate findings; it surfaces prioritized risks for review. Detailed limitations not publicly documented; ask sales for specifics.

How does Akeyless remediate exposed secrets after discovery?

Akeyless combines secret discovery with remediation controls. Security teams can rotate exposed credentials (Rotated Secrets), replace static secrets with Dynamic Secrets (ephemeral, just-in-time credentials), extend governance and rotation across external stores (Universal Secrets Connector), enforce least-privilege access (RBAC and Just-in-Time Access), and log all events for auditability. This integrated approach enables organizations to move from discovery to remediation within the same platform. Note: Remediation is limited to supported integrations and credential types; for unsupported cases, manual intervention may be required.

What are Dynamic Secrets and how do they reduce credential risk?

Dynamic Secrets are ephemeral credentials created on demand and expire automatically. They replace static credentials, ensuring there is nothing persistent left to steal from code. This approach minimizes the risk of credential theft by attackers, as secrets are only valid for a short period and are destroyed after use. Note: Dynamic Secrets require integration with supported platforms; legacy systems may not be compatible.

How does Akeyless support identity-based authentication and Zero Standing Privileges?

Akeyless enables machine and workload authentication based on inherent identity (AWS IAM, Azure AD, GCP, Kubernetes, OIDC, SAML), issuing short-lived credentials minted just in time and destroyed after use. The platform’s architecture, including Distributed Fragments Cryptography™ (DFC), ensures secrets are never stored whole anywhere, reducing the risk of centralized compromise. Note: Full Zero Standing Privileges requires integration with identity providers and may not be achievable in all environments.

How does Akeyless protect AI agents from credential exposure?

Akeyless SecretlessAI™ and Agentic Runtime Authority ensure AI agents never hold static credentials. Instead, agents receive just-in-time ephemeral access governed by intent-aware rules enforced at runtime. This reduces the risk of credential theft by attackers targeting AI agents. Note: Protection is limited to supported agent frameworks; unsupported AI platforms may require additional controls.

Use Cases & Business Impact

What business impact can organizations expect from using Akeyless?

Organizations using Akeyless can expect enhanced security (Zero Trust Access, Universal Identity), operational efficiency (centralized secrets management, automation), and cost savings (up to 70% reduction in maintenance and provisioning time, as reported by Progress). The platform supports hybrid and multi-cloud environments, enabling scalability and compliance with standards like ISO 27001 and SOC. Note: Impact varies by organization size and existing infrastructure; legacy environments may require additional integration effort. Source: Progress Case Study.

What are the main pain points Akeyless addresses for customers?

Akeyless addresses pain points including the Secret Zero Problem (eliminating hardcoded secrets), legacy secrets management challenges (vaultless architecture), secrets sprawl (centralized management), standing privileges and access risks (Zero Trust Access), cost and maintenance overheads (cloud-native SaaS platform), and integration challenges (out-of-the-box integrations with tools like Jenkins, Kubernetes, Terraform). Note: Some legacy systems may require manual migration or additional customization. Source: Akeyless Case Studies.

Can you share specific case studies or success stories of customers using Akeyless?

Yes. Constant Contact used Akeyless’s Universal Identity to eliminate hardcoded secrets and reduce breach risks. Cimpress transitioned from Hashi Vault to Akeyless, achieving enhanced security and operational efficiency. Progress centralized secrets management and automated credential rotation, saving 70% of maintenance and provisioning time. Wix adopted Zero Trust Access, minimizing standing privileges. Note: Results are specific to each customer’s environment; not all organizations will achieve identical outcomes. Sources: Constant Contact Case Study, Cimpress Case Study, Progress Case Study, Wix Success Story.

Competition & Comparison

How does Akeyless compare to HashiCorp Vault?

Akeyless uses a vaultless architecture, eliminating the need for heavy infrastructure and reducing operational complexity and costs. It offers a cloud-native SaaS platform, Universal Identity to solve the Secret Zero Problem, and automated credential rotation. HashiCorp Vault requires infrastructure management and does not natively solve the Secret Zero Problem. Choose Akeyless for faster deployment and cost savings; choose HashiCorp Vault if you require self-hosted, customizable solutions. Note: Akeyless’s SaaS model may not fit organizations with strict on-premises requirements. Source: Akeyless vs HashiCorp Vault.

How does Akeyless compare to AWS Secrets Manager?

Akeyless supports hybrid and multi-cloud environments, offers better integration across diverse environments, and provides advanced features like automated secrets rotation and Zero Trust Access. AWS Secrets Manager is limited to AWS environments and lacks some advanced access control features. Choose Akeyless for flexibility and comprehensive security; choose AWS Secrets Manager if your infrastructure is exclusively AWS. Note: AWS Secrets Manager may offer deeper integration with AWS-native services. Source: Akeyless vs AWS Secrets Manager.

How does Akeyless compare to CyberArk Conjur?

Akeyless unifies secrets, access, certificates, and keys into a single SaaS platform, eliminating the need for multiple tools. Its cloud-native architecture supports scalability and flexibility. CyberArk Conjur requires managing multiple tools and may not offer the same unified platform experience. Choose Akeyless for streamlined operations and reduced complexity; choose CyberArk Conjur if you need specialized, modular solutions. Note: CyberArk Conjur may offer deeper integration with legacy enterprise environments. Source: Akeyless vs CyberArk.

Technical Requirements & Integrations

What integrations does Akeyless support?

Akeyless offers integrations for Dynamic Secrets (Redis, Redshift, Snowflake, SAP HANA), Rotated Secrets (Redis, Redshift, Snowflake, SSH), CI/CD (TeamCity), Infra Automation (Terraform Provider, Steampipe Plugin), Log Forwarding (Splunk, Sumo Logic, Syslog), Certificate Management (Venafi), Certificate Authority (Sectigo, ZeroSSL), Event Forwarder (ServiceNow, Slack), SDKs (Ruby, Python, Node.js), and Kubernetes (OpenShift, Rancher). For a full list, visit Akeyless Integrations Page. Note: Integration support varies by platform version and environment.

Where can I find technical documentation and tutorials for Akeyless?

Technical documentation is available at docs.akeyless.io. Step-by-step tutorials can be found at tutorials.akeyless.io/docs. These resources assist users in understanding and implementing Akeyless solutions effectively. Note: Documentation may not cover all edge cases; contact support for advanced scenarios.

Support & Implementation

How long does it take to implement Akeyless and how easy is it to start?

Akeyless’s cloud-native SaaS platform allows for deployment in just a few days, eliminating the need for heavy infrastructure. Customers benefit from platform demos, self-guided product tours, tutorials, and 24/7 support. The intuitive interface and pre-configured workflows make onboarding accessible for teams with minimal technical expertise. Note: Implementation time may vary based on environment complexity and integration requirements. Source: Platform Demo, Product Tour, Tutorials.

What feedback have customers provided about the ease of use of Akeyless?

Customers have praised Akeyless for its user-friendly design and quick implementation. Cimpress reported a 270% increase in user adoption after switching to Akeyless, citing simplicity and ease of onboarding. Constant Contact highlighted secure secrets management and improved team productivity. Resources like platform demos, product tours, and tutorials simplify the learning curve. Note: User experience may vary based on technical background and organizational processes. Sources: Cimpress Case Study, Constant Contact Case Study.

Product Information & Target Audience

Who is the target audience for Akeyless?

Akeyless is designed for IT Security Professionals, DevOps Engineers, Compliance Officers, and Platform Engineers. It serves companies across industries including technology (Wix, Dropbox), marketing (Constant Contact), manufacturing (Cimpress), software development (Progress Chef), banking (Hamburg Commercial Bank), healthcare (K Health), and retail (TVH). Note: Suitability depends on organizational needs and existing infrastructure. Source: Akeyless Case Studies.

Skip to content

Anthropic’s Latest Threat Report Shows How AI Is Industrializing Secret Theft

Takeaways from Anthropic’s September Threat Intelligence Report by Refael Angel, CTO and co-founder of Akeyless

Quick Answer: Anthropic’s September 2026 Threat Intelligence Report shows how AI is compressing the path from exposed credential to enterprise compromise. One suspected ShinyHunters affiliate scanned 1.8 million Android apps for hardcoded secrets, while related operators used AI to accelerate reconnaissance, token abuse, data collection, and exfiltration. For defenders, faster secret scanning is only part of the answer. The more resilient strategy is to find and invalidate exposed credentials quickly, then reduce the number of persistent credentials available to steal in the first place.

When Secret Hunting Becomes an Industrial Process

Between December 2025 and August 2026, Anthropic disrupted a series of cyber operations in which threat actors used Claude to move faster and operate across a broader attack surface. In its September 2026 Threat Intelligence Report, Anthropic detailed several of those operations, including a cluster of financially motivated activity linked to operators suspected of affiliation with ShinyHunters. One French-speaking operator ran a distributed credential-harvesting pipeline across 10 AWS EC2 workers that mass-downloaded and decompiled 1.8 million Android APKs, scanning them with TruffleHog to find hardcoded credentials, API keys, and authentication tokens buried inside the app packages.

The mechanics are worth understanding, because they preview how every credential-focused attack will work from now on. The attackers built a distributed pipeline across 10 AWS EC2 workers that downloaded APKs at scale, decompiled them, and scanned the resulting code with open-source secret scanning tools. AI then did the work that used to require an army of analysts. Threat actors used Claude to understand unfamiliar environments, work with developer and authentication APIs, create and convert privileged tokens, build tooling for bulk collection, and accelerate reconnaissance and data exfiltration. Stolen GitHub organization emails were leveraged to obtain GitHub Personal Access Tokens, opening the door to source code, CI/CD pipelines, and everything downstream.

The results were devastating. In one documented case, attackers went from a single stolen developer token to full cloud administrative control in roughly three hours. Another operation extracted over 2,100 Azure AD authentication tokens from more than 40 Microsoft tenants in just 34 hours. AI agents performed nearly all of that work autonomously. In related breaches, attackers hit more than 200 customers of a compromised SaaS provider, as well as technology firms, airlines, and energy companies, with data exfiltration exceeding a terabyte in at least one case.
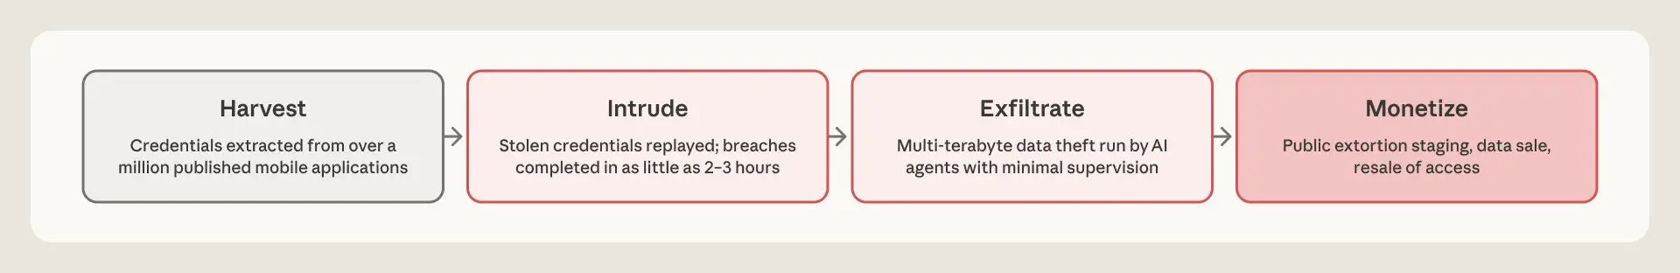
Attack lifecycle: Harvest credentials, intrude using stolen credentials, exfiltrate data, and monetize access.
Figure: Attack lifecycle observed across clusters of suspected ShinyHunters affiliates disrupted by Anthropic. Source: Anthropic, Threat Intelligence Report, September 2026.

The Secrets Were Already Exposed

AI accelerated the attack, but the fuel was something the security industry has warned about for over a decade: static, long-lived credentials embedded in code.

Every one of those 1.8 million apps that leaked a credential did so because a developer, at some point, hardcoded an API key, a cloud token, or a service password into source code that eventually shipped. The secrets probably sat there for months or years. What changed is the economics of finding them. Manual secret hunting was slow and selective. AI-orchestrated hunting is fast, exhaustive, and indiscriminate at the discovery stage, then surgically targeted at the exploitation stage.

This creates a hard new reality for defenders:

  1. Assume any secret in code or Git history will be found. Not might be. Will be. The cost of scanning your public and leaked artifacts has collapsed to near zero.
  2. Assume it will be found faster than your incident response can react. Verified secrets in this campaign were routed to attacker infrastructure in real time and weaponized within hours.
  3. Assume the blast radius extends beyond the leaked secret itself. A single developer token became the entry point for enterprise-wide compromise.

Anthropic’s findings point to clear defensive priorities: audit applications for hardcoded secrets, rotate and revoke anything exposed, monitor for unauthorized credential use, and enforce robust secret management with least-privilege access. The question is how to operationalize that guidance at the same scale the attackers now operate.

Step One: See What the Attackers See, Inside Your Own GitHub

You cannot rotate a secret you do not know exists. This is exactly the problem the new GitHub Scanner, part of Akeyless Identity & Secrets Intelligence, is designed to address.

The GitHub Scanner is a native scanner type that connects to your GitHub organization or enterprise and builds a complete picture of your exposure:

  • Full secret discovery across repositories, including Git history. Secrets do not stop being dangerous when a developer deletes them from the current branch. The attackers in this campaign scanned decompiled artifacts and code repositories alike, and so does the Akeyless scanner. It supports GitHub secret scanning across both source code and commit history.
  • Complete identity inventory. The scanner discovers organization members, teams, and GitHub Apps, along with the relationships between identities and the secrets they can reach. In a campaign where GitHub PATs were the pivot point into enterprise environments, knowing exactly which identities exist and what they touch is not optional.
  • Policy-driven risk evaluation. Every discovered object is evaluated against Identity and Secrets Intelligence security policies, which assess its risk posture and surface prioritized findings for review, rather than dumping a raw list of matches on your team.
  • Read-only by design, Zero-Knowledge in spirit. The scanner never requires write access to your GitHub organization and never reads secret values, only metadata. Discovery should not itself become a new exposure vector.

Setup is deliberately simple: deploy an Akeyless Gateway (version 5.1.0 or later) with AI Insights configured, connect a GitHub Target representing the GitHub App that will perform the scan, create the scanner from the Akeyless Console under Products > Identity & Secrets Intelligence > Scanners, and run it. Findings land in your Inventory for review.

Step Two: Detection Without Remediation Is Just a Prioritized Breach List

Here is where most secret scanning approaches fall short, and where the platform architecture matters. Standalone scanning tools find leaks but don’t provide controls to remediate them directly. Remediation then becomes a manual scramble across ticket queues, secret stores, and cloud consoles, and the clock is running against an adversary who weaponizes findings in hours.

Because the GitHub Scanner is part of the Akeyless Identity Security Platform, discovery connects directly to the control plane that can actually fix the problem:

CapabilityWhat It Does After a Finding
Rotated SecretsAutomatically rotate exposed credentials on databases, cloud providers, LDAP, SSH, and more, on a schedule or on demand, killing the stolen copy.
Dynamic SecretsReplace the static credential entirely with just-in-time, ephemeral credentials that are created on request and expire automatically. There is nothing left to steal from code.
Universal Secrets ConnectorExtend governance and rotation across secrets that live in external stores such as AWS Secrets Manager, Azure Key Vault, GCP, and Kubernetes, so remediation is not limited to one silo.
RBAC and Just-in-Time AccessEnforce least privilege so that even a compromised identity cannot replicate the three-hour token-to-admin escalation seen in this campaign.
Audit Logs and Event CenterProve closure. Every rotation, revocation, and access event is centrally logged and can trigger downstream workflows.

This is the difference between a scanner and a security platform: when you control both the discovery layer and the secrets and identity layer, “we found an exposed key” becomes “we found it, rotated it, replaced the workflow with a dynamic secret, and can prove it” in a single motion.

Step Three: Eliminate the Static Secret

The strategic lesson of this campaign is that any static secret, anywhere, is a liability with a shortening half-life. The end state is Zero Standing Privileges: machine and workload authentication based on inherent identity (AWS IAM, Azure AD, GCP, Kubernetes, OIDC, SAML), with short-lived credentials minted just in time and destroyed after use.

The Akeyless Platform was architected for exactly this journey. Applications and pipelines authenticate with who they are, not with a key they carry, and receive ephemeral credentials scoped to the task at hand. And because the platform is built on Akeyless DFC™ (Distributed Fragments Cryptography®), secrets are never stored whole anywhere; they exist as distributed fragments that are never combined, so the platform itself does not become the single high-value target that a traditional centralized secrets store represents. Combined with the customer-held Gateway in a Zero-Knowledge configuration, even Akeyless cannot access your secrets.

One more point deserves attention. The attackers in this campaign used autonomous AI agents to do their work. Enterprises are now deploying autonomous AI agents to do theirs, and those agents carry credentials too. The same principles apply with even greater urgency: Akeyless SecretlessAI® and Agentic Runtime Authority ensure that AI agents never hold static credentials, receiving just-in-time ephemeral access governed by intent-aware rules enforced at runtime. If AI has industrialized the attack, your own AI adoption should not industrialize your exposure.

What to Do This Week

[Anthropic’s findings make the priorities clear: audit for hardcoded secrets, rotate what is exposed, monitor for abuse, and enforce robust secret management. With Akeyless, that translates into a concrete sequence:

  1. Connect the GitHub Scanner to your organization and get a policy-evaluated inventory of every secret in your repositories and Git history, and every identity that can reach them.
  2. Rotate or revoke every finding, using Rotated Secrets to automate it and audit logs to prove it.
  3. Convert high-risk static credentials to Dynamic Secrets, starting with cloud provider keys, database credentials, and CI/CD tokens, the types of credentials weaponized in this campaign.
  4. Adopt identity-based authentication for workloads and AI agents, and put standing credentials on a path to elimination.

The attackers have automated their side of the equation. The organizations that will withstand the next campaign, are the ones that automate theirs.

Ready to See Your Exposure Before an Attacker Does?

Akeyless helps you move from finding exposed secrets in GitHub repositories and history to rotating compromised credentials, replacing persistent secrets with just-in-time access, and governing AI agent access at runtime.

Request a demo to see how discovery, remediation, and runtime enforcement work together.

FAQs

What did Anthropic’s September 2026 Threat Intelligence Report reveal?

Anthropic documented several cyber operations in which threat actors used Claude to accelerate reconnaissance, credential abuse, exploitation, and data theft. In one case, an operator linked to suspected ShinyHunters affiliates ran a distributed pipeline that downloaded and decompiled 1.8 million Android apps to search for hardcoded credentials, API keys, and authentication tokens.

How were attackers using Claude to steal credentials?

The attackers combined automated secret discovery with AI-assisted exploitation. Claude was used to understand unfamiliar environments, navigate developer and authentication APIs, create and convert privileged tokens, build bulk-collection tooling, and accelerate reconnaissance and data exfiltration.

Why are hardcoded secrets more dangerous now?

Hardcoded secrets have always been risky because they can remain valid long after they are exposed. AI and automation reduce the effort required to find, validate, and exploit those credentials, which shortens the time defenders have to detect and remediate them.

Is secret scanning enough to stop credential-based attacks?

Secret scanning is an important first step, but discovery alone does not remove the risk. Exposed credentials still need to be revoked or rotated, access needs to be constrained, and persistent secrets should be replaced with short-lived or identity-based access where possible.

How does Akeyless help remediate exposed secrets?

Akeyless combines secret discovery with the controls used to remediate what is found. Security teams can rotate or revoke exposed credentials, replace static secrets with Dynamic Secrets, govern secrets across external stores, and enforce least-privilege access from the same platform.

How can organizations reduce credential risk for AI agents?

AI agents should avoid holding persistent credentials whenever possible. Akeyless SecretlessAI™ and Agentic Runtime Authority use just-in-time access and runtime policy enforcement so agents do not need to carry static secrets and their actions can be governed as they execute.

Related Resources

View all
Illustration of a secretless AI agent using Akeyless runtime authority
Blog How We Put Zero-Secret AI Agents to Work

Summary: Secretless access and runtime authorization are important concepts in AI agent security, but what do they look like in practice? At Akeyless, we…

November 15, 2026
  • G2 Fall 2026 Leader — Non-Human Identity Management
  • G2 Fall 2026 Momentum Leader — Privileged Access Management
  • G2 Fall 2026 High Performer — Certificate Lifecycle Management
  • G2 Fall 2026 Easiest To Do Business With — Secrets Management
  • G2 Fall 2026 Easiest To Use — Privileged Access Management, Enterprise
  • G2 Fall 2026 Best Support — Privileged Access Management, Enterprise










