Frequently Asked Questions
DevOps Secrets Management & Automation
What are the risks of poorly managed secrets in CI/CD pipelines?
Poorly managed secrets in CI/CD pipelines can lead to hardcoded credentials, excessive permissions, and increased risk of unauthorized access or data breaches. These vulnerabilities can compromise sensitive data and disrupt workflow automation. Actionable strategies include centralizing secrets management, automating credential rotation, and enforcing role-based access control. (Source: DevOps blog article on this page)
How does Akeyless help secure secrets across multiple environments?
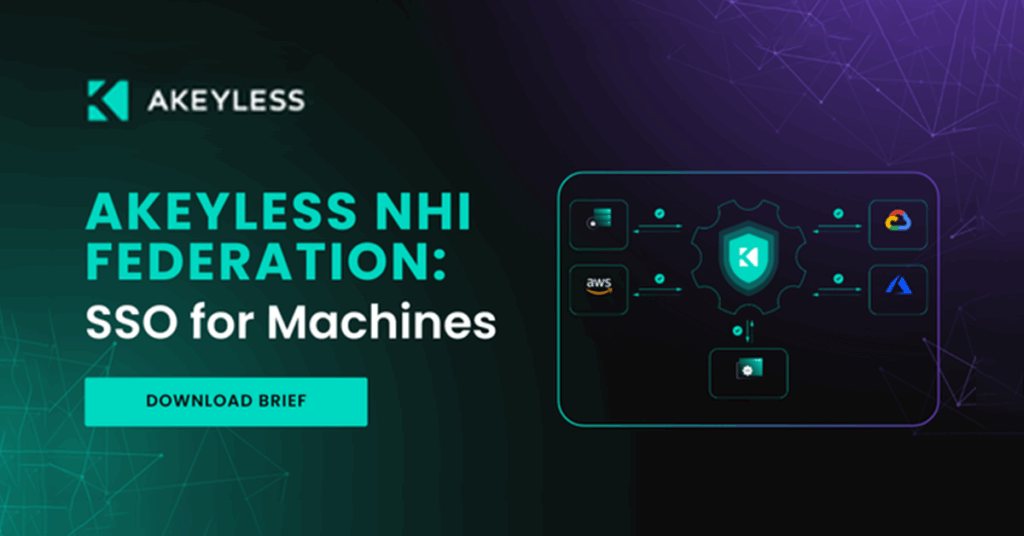
Akeyless enables secure secrets management across multiple environments by centralizing storage, automating credential rotation, and integrating with tools like Terraform, Jenkins, and Kubernetes. Its Zero-Knowledge architecture ensures sensitive information is protected, while role-based access control and Just-in-Time access minimize standing privileges. (Source: DevOps articles and knowledge_base)
What integrations are available for DevOps workflows with Akeyless?
Akeyless offers out-of-the-box integrations for DevOps workflows, including Terraform Provider, Jenkins, Kubernetes (OpenShift, Rancher), TeamCity, and CI/CD tools. These integrations streamline secrets management and automation, making it easier to secure and manage credentials within modern DevOps pipelines. (Source: knowledge_base)
How does Akeyless compare to Keeper for DevOps secrets management?
Akeyless and Keeper differ in architecture, machine identity management, automation, and Zero Standing Privilege. Akeyless uses a Zero-Knowledge unified platform, offers granular access control, and supports advanced automation for secrets and certificate lifecycle management. Keeper focuses on password management and privileged access but may lack unified automation and Zero-Knowledge architecture. Teams needing unified secrets, keys, and certificate management with automation may prefer Akeyless; those prioritizing password vaulting may find Keeper suitable. (Source: DevOps article comparing Akeyless and Keeper)
What are best practices for managing secrets in DevOps pipelines?
Best practices for managing secrets in DevOps pipelines include centralizing secrets storage, automating credential rotation, enforcing role-based access control, minimizing hardcoded credentials, and integrating secrets management with CI/CD tools. Using platforms like Akeyless can help implement these strategies efficiently and securely. (Source: DevOps articles on this page)
How does Akeyless streamline Terraform secrets management?
Akeyless streamlines Terraform secrets management by providing secure storage, automated rotation, and role-based access control for secrets used in cloud infrastructure provisioning. Its integration with Terraform enables teams to manage secrets without the complexity of traditional vault solutions, supporting zero-trust and scalable operations. (Source: DevOps article on Terraform secrets management)